

Blocks your Cursor agent's wrong moves before they land.
Chock policies as Cursor plugins — guards ship a real beforeShellExecution deny hook, gates judge the write at preToolUse.


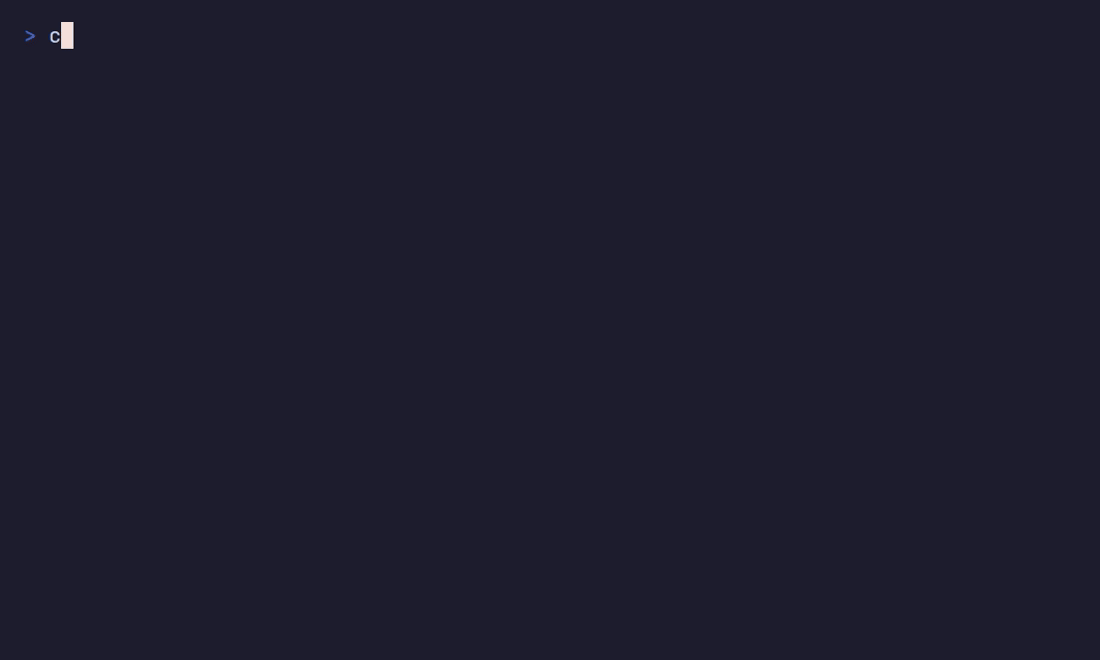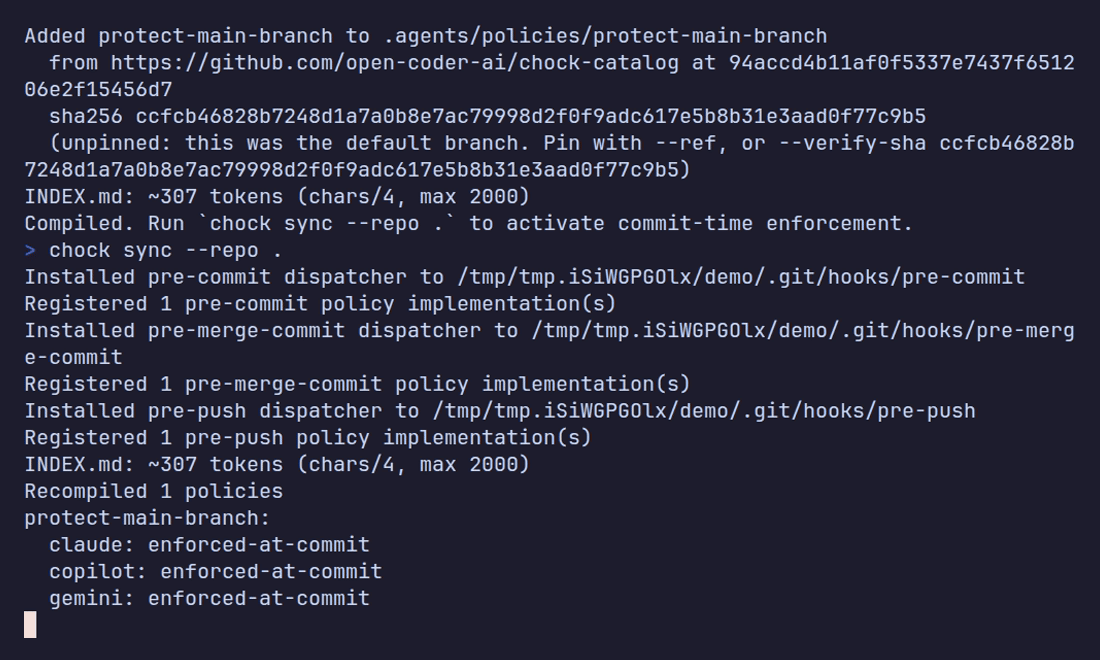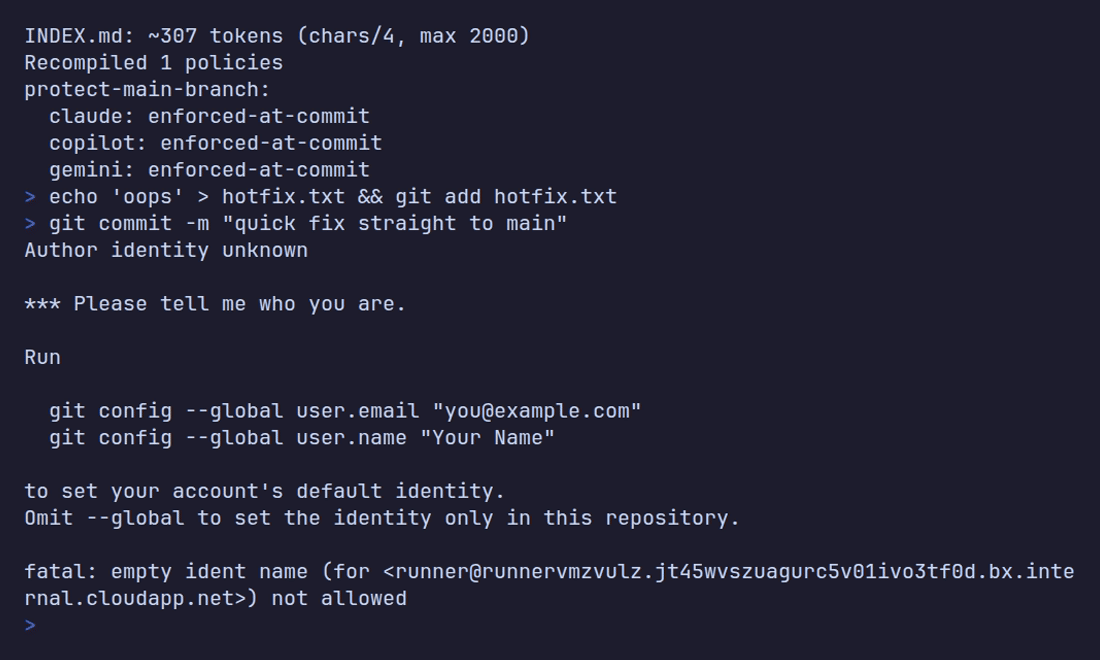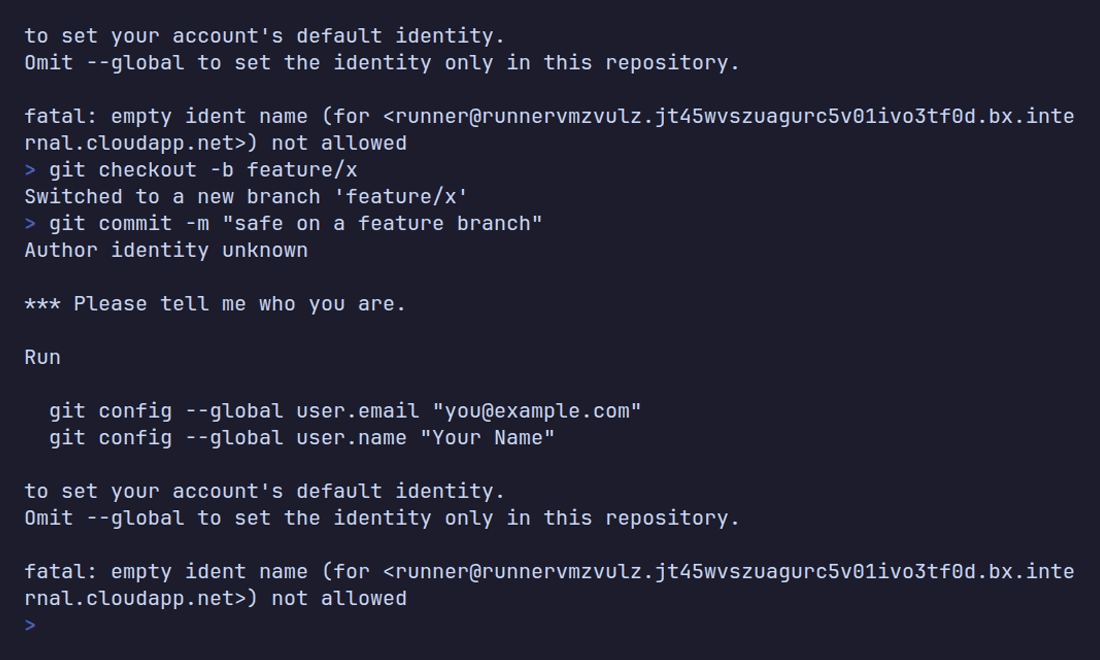
An agent running in your editor can already touch your shell, your git history, and your CI
config. You want it to move fast without being the reason a stray terraform destroy
actually happens. Telling it to be careful in a prompt is not a guarantee; a plugin that can
refuse the command is closer to one — a matched destructive command is denied in the editor
before it runs, witnessed on a real Cursor install (2026-08-24), with benign commands in the
same session still allowed.
This marketplace: no chock on the machine. Each policy is its own plugin, republished with
every chock release. You need Python 3.11+, git and a bash (Git for Windows includes one). Cursor reads this
repository as a plugin marketplace via .cursor-plugin/marketplace.json:
# Team marketplace: Dashboard -> Plugins -> Add Marketplace -> Import from Repo
#   https://github.com/open-coder-ai/chock-cursor-plugins
# Local install of one plugin (developer flow):
#   copy cursor/<plugin-id>/ to ~/.cursor/plugins/local/<plugin-id>/ and reload Cursor
The builder: one plugin, needs chock. Pick the policies you want at
https://chock.sh/coding/builder/; it gives you one command that builds a single
chock-guardrails plugin on your machine from
chock-catalog. That command needs
pip install chock:
pip install chock
chock install --selection <code> --client cursor --apply
<code> is the selection code the builder shows for your choice. Cursor has no command to run
for a local plugin, so the output tells you to run Developer: Reload Window; then check the
plugin under Customize.
Use one route for a given policy, never both. Every copy of a plugin runs its own hook, so a policy installed from both places runs twice. To switch a policy from one route to the other, remove it from the first route before installing it from the second:
- Team marketplace import: in Cursor, open Dashboard -> Plugins & MCPs, find this repository under Team Marketplaces and remove it (an admin action on Enterprise). Then open Customize and remove each plugin you installed from it; a plugin set to Required cannot be uninstalled until it is changed in the marketplace's settings. See Cursor's plugin docs.
- Local copy: delete each
~/.cursor/plugins/local/<id>/folder you copied fromcursor/<id>/, then run Developer: Reload Window (or restart Cursor).
Each link opens the builder with that one policy chosen for Cursor. The selections pin
catalog.ref to chock-catalog commit e885f918a335e20dfddb4fad0331d4d5b4c5eb43, so a link builds the
policy version at that commit, which can be newer than the one listed in PLUGINS.md.
"Published here as" is what PLUGINS.md says for this client.
| Policy | Published here as | Builder |
|---|---|---|
agent-discipline |
advisory | Open in the builder |
block-curl-pipe-sh |
enforces | Open in the builder |
block-destructive-commands |
enforces | Open in the builder |
block-invisible-unicode |
enforces | Open in the builder |
block-no-verify |
enforces | Open in the builder |
block-test-skips |
enforces | Open in the builder |
block-unapproved-egress |
enforces | Open in the builder |
block-unguarded-agent-spawn |
enforces | Open in the builder |
block-wildcard-agent-permissions |
enforces | Open in the builder |
chock-mise |
advisory | Open in the builder |
code-safety |
advisory | Open in the builder |
context-hygiene |
advisory | Open in the builder |
firecrawl-fallback-only |
advisory | Open in the builder |
git-safety |
advisory | Open in the builder |
guard-memory-writes |
enforces | Open in the builder |
injection-defense |
advisory | Open in the builder |
java-security |
enforces | Open in the builder |
limit-diff-size |
advisory | Open in the builder |
memory-discipline |
advisory | Open in the builder |
no-a11y-regression |
enforces | Open in the builder |
pin-github-actions |
enforces | Open in the builder |
protect-agent-config |
enforces | Open in the builder |
protect-ci-workflows |
enforces | Open in the builder |
protect-commit-privacy |
enforces | Open in the builder |
protect-main-branch |
advisory | Open in the builder |
protect-test-integrity |
enforces | Open in the builder |
rtk-dangerous-actions-blocker |
enforces | Open in the builder |
scan-secrets |
enforces | Open in the builder |
token-efficiency |
advisory | Open in the builder |
verify-dependency-exists |
enforces | Open in the builder |
verify-mcp-allowlist |
enforces | Open in the builder |
Every file here is compiled from policy sources in chock-catalog by chock. Pull requests against this repository are closed automatically — open them against the catalog instead.
- Generated only: CI regenerates from the pinned catalog and fails on any difference.
- Byte-identical guards: each guard script is a verbatim copy of its policy's source in the catalog, and the hook adapter a verbatim copy of its framework source.
- Best-effort, not a boundary: guards are pattern-based filters; see SECURITY.md.
- Tested upstream, and gated: every policy ships an eval suite
(
base/<policy>/evals/suite.yaml) in the catalog, and the publish workflow runschock checkandchock check --only evalsbefore packaging anything — a policy whose evals fail cannot reach this repository. The tests live in the catalog because the policy source does; this repository is compiled output. - This README is hand-written, as are
SECURITY.mdand the workflows under.github/, so they sit outside the generated-only guarantee.
Nothing above asks for trust that cannot be checked. This rebuilds the published tree from source and compares it with what is committed here:
git clone https://github.com/open-coder-ai/chock-cursor-plugins dist
git clone https://github.com/open-coder-ai/chock-catalog catalog
git clone --branch "$(tr -d '[:space:]' < catalog/.framework-ref)" \
  https://github.com/open-coder-ai/chock framework
pip install ./framework
chock plugin build --repo catalog --policies-dir base --format cursor --out-dir dist
chock marketplace build --dist dist --tree cursor
git -C dist diff --exit-code && git -C dist status --porcelain
Silence from both git commands means this repository is byte-identical to a fresh build
from the catalog. The framework ref comes from the catalog's own .framework-ref, which is
what the publish and Generated-only workflows read, so this recipe cannot drift from the
release a tree was actually built with.
chock-market.lock records a sha256 per published plugin directory, so one package can be
checked without rebuilding the rest.
If you are listing these plugins in a marketplace, pin both a tag and the full commit SHA. The tag names the release; the SHA is what holds the reviewed bytes still.
| You want to | Go to |
|---|---|
| Fix or add a policy | chock-catalog — it reaches every client from there, including this one |
| Report that a guard did or did not block on your Cursor version | an issue on chock, which records the witnessed-blocking claims these packages carry; "it fails open where you say it fails closed" is the most useful result you can send |
| Report a bug in how packages are generated | chock, where the emitter lives |
| Fix this README | here — it is hand-written, not generated |
| agentseam | the primitives — one handler API and a verified capability matrix across 16 agents |
| chock | the compiler — one policy into git hooks, CI gates and native pre-tool hooks |
| chock-catalog | the policies — 42, each labelled enforced or advisory, with replayed evals |
| context-report | the evidence — a signed report of whether an agent artifact actually works |
| chock-threat-intel | the threat ledger the catalog's policies answer to |
| chock-{claude,cursor,copilot,codex}-plugins | the catalog, packaged for each agent's plugin format (generated) |
| chock-quickstart · chock-example | template repos: what chock init leaves behind, and a full adoption |
Apache-2.0, same as the framework and the catalog.