


M.S. Computer Science at Northeastern University, building reliable AI applications and scalable backend systems. Seeking a Summer 2027 software engineering / AI internship.
Five years of production experience before the degree: an LLM Text-to-SQL agent and a CRM platform at an industrial-supply company, and lead-routing and streaming-analytics services at a real-estate brokerage.


| Project | What it does | Stack |
|---|---|---|
QueryGuard  |
Text-to-SQL service that treats model output as untrusted: schema retrieval, sqlglot AST validation, and row-level authorization injected server-side. 25-case eval suite runs in CI on Python 3.9–3.13. |
FastAPI · sqlglot · SQLAlchemy · SQLite |
A sales rep asks for "my customer orders". They never say which customers are theirs,
and the model is never asked to scope the query. The customer_assignments predicate in
the generated SQL is injected by the server after validation — authorization is a query
transformation, not a prompt instruction.
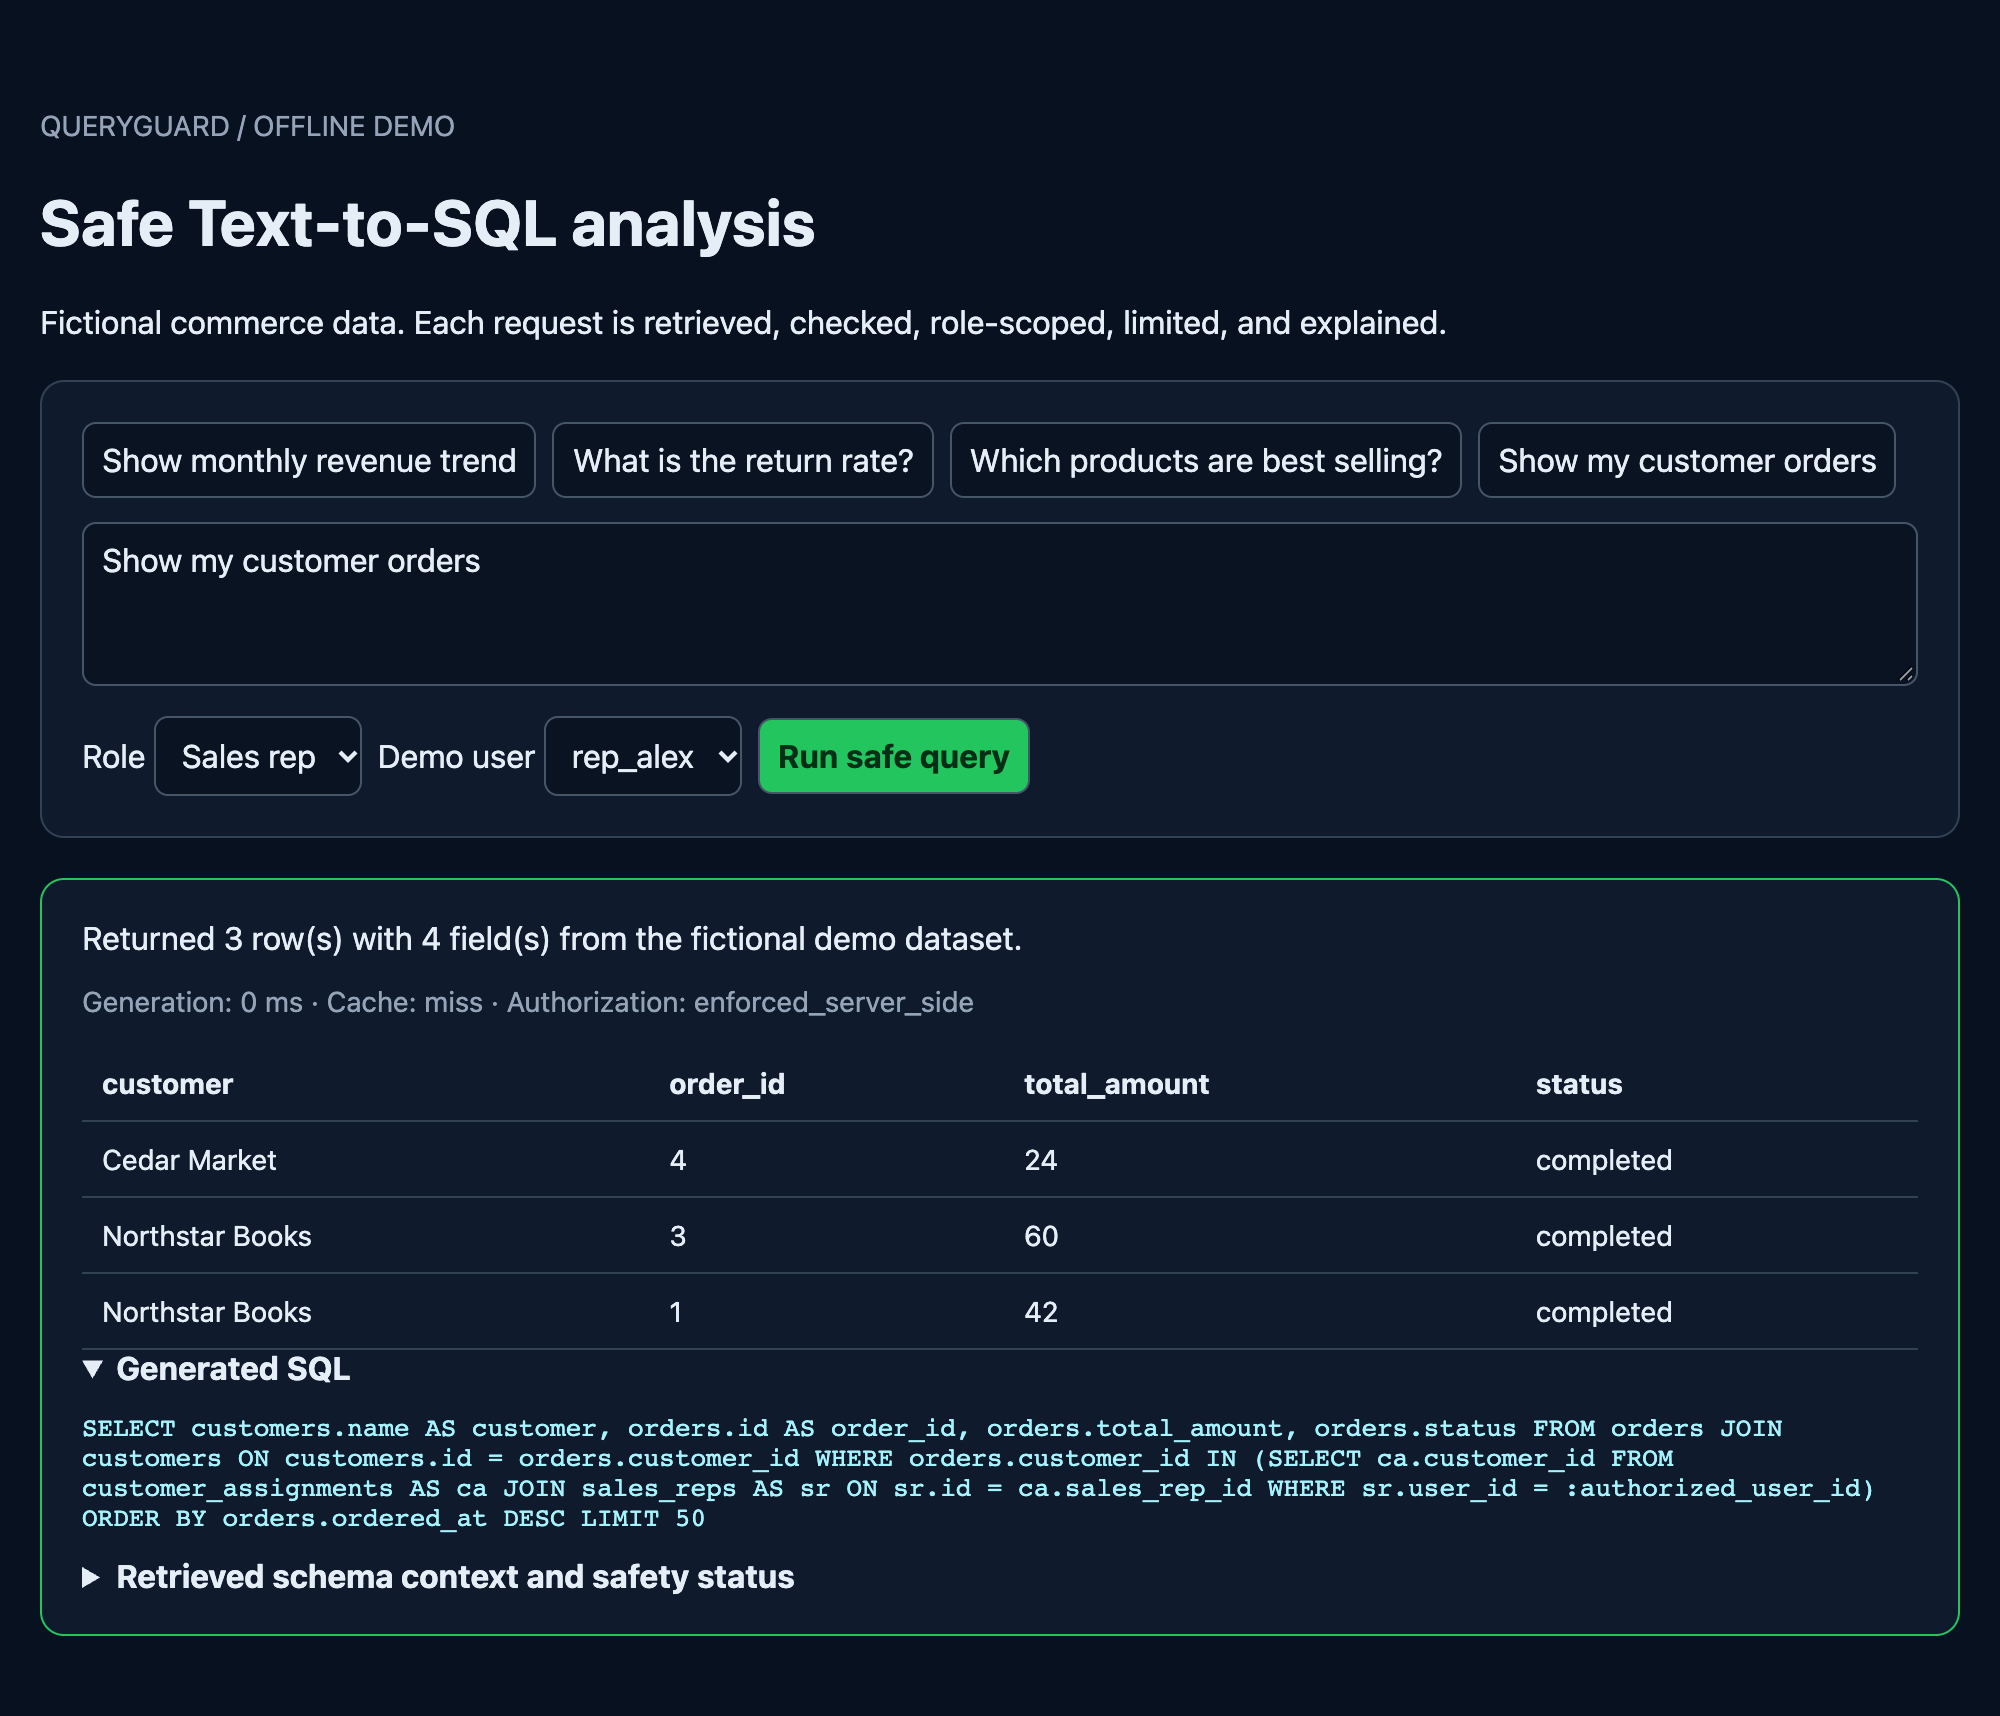
On the repository's deterministic fictional dataset the 25-case suite reports execution accuracy 1.0, zero authorization violations, and a 1.0 safety interception rate. Those numbers describe this demo harness, not general Text-to-SQL model quality — the README is explicit about the scope and the limitations.
Updated September 2026
- Extending QueryGuard's evaluation suite with an adversarial subset covering prompt-injection attempts against the authorization layer.
- Building an event-driven backend service with load-test and observability evidence.
- Daily algorithm practice in neetcode-submissions.
- AI systems: LLM applications, retrieval, evaluation, and safety guardrails
- Backend systems: APIs, data modeling, event-driven services, caching, and observability