Repository navigation
feat(buzz-db): run push enqueue and channel TTL refresh in app code - #8135
Conversation


6b5a117 to
1eb11bd
Compare
 GitHub Actions
Error

 wpfleger96
left a comment
wpfleger96
left a comment
There was a problem hiding this comment.
🤖 Thanks, Luke. Nothing here blocks.
I compared both producers with the trigger functions. The push enqueue uses the same kind allowlist, the same shared buzz_push_gate key (the Rust Uuid display matches ::text), the lock as its own statement before the lease check, the same lease predicate, and it fails closed. The TTL refresh uses the same shared lock key, the same ttl_seconds/archived_at/deleted_at filters, and skips 9007. The per-channel savepoint behaves like the plpgsql EXCEPTION block: rolling it back releases the advisory and row locks, and 57014 still rejects the event. Every non-test INSERT INTO events under crates/*/src is one of the seven hooked writers or one of the two rolled-back probes. Each ON CONFLICT DO NOTHING path runs the hook only after a real insert. The parameterized path enqueues inside parameterized_replace and records the channel only after release, which also covers replacements. commit() is the only way an AdmittedTx commits, and conn() is crate-private, so nothing outside the crate can wrap an insert in a savepoint that would leave a recorded channel behind. The deferred floor guard takes no locks, refreshes run in sorted order, and FK KEY SHARE doesn't conflict with the refresh's NO KEY UPDATE, so I don't see a new lock cycle.
All four contract arms pass by name in PostgreSQL Domain / PostgreSQL Tests, and the 16 source-policy tests run in Rust / Unit Tests. Against a local relay at this head, in both app-only and dual mode, a kind 9 advanced a TTL channel's deadline and left a permanent channel's NULL. Each message with an active lease got exactly one queue row. Missing, expired, and endpoint-disabled leases got none, and an exact replay changed nothing. Eight concurrent posts to one TTL channel all committed with no deadlock or lock timeout. Making enqueue_push_match a no-op fails both app-only arms and leaves both dual arms green, as expected. The full buzz-db Postgres lane is 464/464.
Optional
observability_source.rsL1545–1549:runs_event_follow_upsmatches raw text, andfunction_sliceskeeps comments and strings, so a writer whose hook is commented out (// crate::store::event_follow_up::after_admitted_insert() still passes and still counts toward the floor of seven. The seven writers you have today are covered anyway, because the app-only arms exercise every writer that carries a channel or a push kind. The gap is a future writer. Matching the hook only outside//comments and string literals (the lexer incfg_test_item_lenalready skips both) plus fixtures for a commented-out hook and a hook name inside a string would close it.event_follow_up.rsL123–147: an ephemeral channel's row lock is now held throughRELEASE SAVEPOINTand theCOMMITround trip, so writers to a busy TTL channel queue behind about two more client round trips each than with the trigger. The latency numbers in the description are single-client, so they don't measure that. The burst above was fine, but it's worth watching once this is on real pods.- While both producers run, a refresh that hits
lock_timeoutis retried by the trigger insideCOMMIT, so the worst case waits twice and the failure counter can count a refresh the trigger then completes. That goes away with the retirement PR, which might say so. - The description has no
buzz-review-completedline.
|
Thanks Will. (1) Fixed at |
GitHub Actions
Inactive
GitHub Actions
Inactive
 github-actions
Bot
added
the
codex-security-review-current

🔐 Codex Security Review
Review SummaryOverall Risk: NONE
FindingsNo concrete security, correctness, or reliability findings were identified. Notes
Generated by Codex Security Review | |
github-actions
Bot
removed
the
codex-security-review-current
GitHub Actions
Error
wpfleger96
left a comment
wpfleger96
left a comment
There was a problem hiding this comment.
🤖 Thanks, Luke. The comment/string masking fixes the false pass I raised last time, and nothing here blocks.
runs_event_follow_ups now matches on masked text, so a hook in a // comment, a nested /* */, a string, a string with escaped quotes, or a raw string no longer counts. inserts_events_row still reads the original text, which it has to since the SQL is inside literals. If the masker gets something wrong, it hides a real hook rather than inventing one, so the test fails loudly instead of passing. All seven writers still have real hooks at this head (two in event.rs, two in replaceable.rs, one each in channel_members.rs, push.rs, and relay_members.rs), and the fixture test and the production scan both pass by name in Rust / Unit Tests.
Optional
-
observability_source.rsL1427–1440 and L953–979:strip_cfg_test_itemsandfunction_slicesstill find attributes and signatures in the unmasked text, and the masker only runs on fragments afterward, so it can't see a comment or string that opened before the fragment. Two ways that slips, both older than this change and neither hitting today's writers:- a
#[cfg(test)]at the start of a line inside a multiline/* */gets treated as a real attribute. The item scan starts after the marker, never sees the opening/*, and strips the next production function through its closing brace, so a new writer can drop out while the floor of seven still holds. - a multiline raw string with a line starting
fn example() {splits the function. If the quoted example contains the hook and the real insert comes after the literal, the second slice starts inside the string, sees the quoted hook as code, and passes.
Masking the whole file once and finding attributes and signatures in that view (offsets match the original, so SQL checks can keep reading the original) would close both. Fixtures for both cases would pin it.
- a
-
L1710–1763: the fixtures cover less than the description says. Nothing pins
cr", plainb"/c"strings, raw strings with zero or several#, or escaped char literals, so droppingcrhandling wouldn't fail any test. A small table of inputs and their masked output would cover it, or the description could claim less.
GitHub Actions
Error
|
Thanks Will, both done at |
wpfleger96
left a comment
wpfleger96
left a comment
There was a problem hiding this comment.
🤖 Thanks, Luke. Both optional items from last round are in, and nothing here blocks.
strip_cfg_test_items and function_slices now find markers and signatures in one masked view of the whole file. A #[cfg(test)] inside a multiline /* */ strips nothing, and an fn line inside a raw string no longer splits a function. The new fixtures pin both, and masker_blanks_every_literal_form_and_keeps_code covers the literal forms. Locally, four edits to a real enqueue_push_match call each fail every_production_event_insert_runs_the_follow_up_hook: commenting it out, moving it into a string, moving it into a raw string, and deleting it. Each revert brings all 17 source tests back to green. All 17 also pass by name in Rust / Unit Tests.
Optional
observability_source.rsL1560–L1571: with the whole file masked, a misread character literal can now hide a real signature. That changes what I said last round, that a masker mistake can only make the test fail. Char literals are recognized only as one byte or a two-byte escape, so'é'and'\u{1f}'aren't consumed as tokens. Inlet _ = ['é','"'];, the closing quote, the comma, and the next quote read as a new char literal, the"opens a string, and the mask runs through the next function's signature. A hooked writer followed by an unhooked one then becomes one slice with no violation; the scanner atfbc9a598flags it. The same misalignment can hide a real#[cfg(test)]. rustfmt writes that as'é', '"', which masks correctly, so it only bites in code rustfmt doesn't format, and nothing today hits it. Consuming whole char tokens (UTF-8 characters and\x/\u{…}escapes, with lifetimes still falling through), plus a fixture for that input, would close it.- The description has no
buzz-review-completedline.

Every production INSERT INTO events now calls store::event_follow_up:

- enqueue_push_match mirrors the events_enqueue_push_match trigger: same
  kind allowlist, SHARED buzz_push_gate lock as its own statement, same
  lease predicate, ON CONFLICT DO NOTHING, and errors reject the event.
- AdmittedTx records each channel that received an event and refreshes
  its ttl_deadline as the last statement before COMMIT, one savepoint per
  channel in sorted order. A failure is rolled back, logged, and counted
  (buzz_db_channel_ttl_refresh_failures_total{reason}); the event still
  commits. A cancelled statement still rejects, as under plpgsql.

The triggers stay in place, so both producers run until they are retired.
A source policy test requires every non-test events insert to run the
hook, and the follow-up contract suite runs dual and app-only (triggers
dropped in the disposable database) on desired and migration schemas.

Refs BUZZ-176

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
…aths

Review follow-ups for the app-owned push enqueue and TTL refresh:

- The follow-up source policy strips each #[cfg(test)] item instead of
  cutting the file at the first one, so production code after a test-only
  helper is scanned. It matches the insert in any case, across line
  breaks and string continuations, with or without public., and scans
  every crate's src.
- The contract suite asserts that a lock-timeout TTL failure increments
  buzz_db_channel_ttl_refresh_failures_total{reason="lock_timeout"} once,
  and that a cancelled refresh (57014) rejects the event.
- The TTL refresh drops its separate ttl_seconds read: the UPDATE's own
  filter never locks a permanent channel's row. The doc now states the
  ephemeral row lock spans the remaining refreshes and COMMIT.
- One key builder per lock protocol: push_gate_lock_key and
  channel_ttl_lock_key are used by both the SHARED and EXCLUSIVE sides.
- The shared push-gate wait is observed as LockType::PushGate, cancel
  detection uses DbError::is_statement_cancelled, and
  refreshes_channel_ttl is renamed ttl_refresh_channel.

Refs BUZZ-176

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
A #[cfg(test)] mention inside a comment no longer strips the production
item that follows it. Correct the dual-arm note on the 57014 contract.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
A string-literal escape between INSERT INTO and events no longer hides
an unhooked writer from the follow-up policy.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
#8130 replaced AdmittedTx's Deref with a crate-private conn() accessor,
so the push producer's call sites now pass tx.conn() explicitly. The
source-policy fixtures follow the same shape.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
#8130 made AdmittedTx's connection crate-private, so an integration test
can no longer run SET LOCAL timeouts or in-transaction reads on it. Move
the contract suite into store/ as a #[cfg(test)] module, next to
artifact_postgres_tests, where it uses AdmittedTx::conn().

Drop the line-based strip_cfg_test_items that #8130 added to the source
policy; the literal-aware one from this branch covers its fixture test.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Scanning admitted_tx.rs through strip_cfg_test_items hid an indented
#[cfg(test)] forging constructor from the count. Scan the raw source
and pin it with a fixture that must report the forge.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
The follow-up policy matched the hook name as raw text, so a commented-out
or quoted hook passed and counted toward the writer floor. Match only code,
using one comment/literal masker that the cfg(test) item scanner now
shares.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
…the masker

Fixtures for a hook inside a nested block comment and after an escaped
quote, so disabling either branch fails the policy test. Recognize br""
and cr"" raw literals, pinned by a raw byte string ending in a backslash.
Refresh the strip_cfg_test_items doc.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
A hook name inside a raw string must not count as a call, so removing the
masker's raw-string branch now fails the fixture test.

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Mask the whole file once and look for #[cfg(test)] markers and fn
signatures in that view, so a marker inside a multiline block comment no
longer strips the next production function, and an fn line inside a
multiline raw string no longer splits a function. Pin both with policy
fixtures, and add a table test for each literal form the masker handles
(raw strings with zero or several #, br/cr prefixes, b/c strings,
escaped char literals, raw identifiers, lifetimes).

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
c5a06a8 to
184cbb2
Compare
GitHub Actions
Inactive
github-actions
Bot
added
the
codex-security-review-current
wpfleger96
left a comment
wpfleger96
left a comment
There was a problem hiding this comment.
🤖 Thanks, Luke. The char-literal fix from last round is in, the rebase onto #8178 is clean, and nothing here blocks.
char_literal_end now consumes whole char tokens: UTF-8 scalars, simple escapes, \x.., and \u{…}. Lifetimes and labels still fall through, and it can't slice off a char boundary. The three new fixtures ('é', '\u{1F600}', '\x7f') each fail if the old two-arm match is put back and pass with the new helper. All 17 source tests pass by name in Rust / Unit Tests. Locally at this head, the full PostgreSQL suite passes too, including the four follow-up contracts, all 18 push tests, and the TTL/activation-race tests.
Commits 2–11 are unchanged from the last round. Commit 1 only drops the backfill comment that #8178 removed, and the new "no wake was owed" wording in event_follow_up.rs matches main: activation still takes the push gate exclusive, and an event holds it shared to transaction end.
Optional
observability_source.rsL1580–L1583: the 9-byte cap on escapes misses Unicode escapes with underscores, which Rust allows after each hex digit (reference).'\u{0_0_0_0_7_b}'returnsNone, so ina('\u{0_0_0_0_7_b}','{') {}its closing quote reads as the start of the next literal and the{stays unmasked. Inside a#[cfg(test)]item that brace can make the strip run into production code. Nothing hits it today, and the old masker had the same gap. Parsing the\u{…}grammar instead of capping bytes, plus a fixture with adjacent literals, would close it.- The description has no
buzz-review-completedline.

Push enqueueing previously ran inside the message transaction, so a push
lock or database error could block or reject a message. Configured relay
writers now submit bounded best-effort work only after commit. A
dedicated connection and bounded queue isolate enqueue waits and
failures from message-write connections. Overload, errors, process loss,
or shutdown may drop a notification; the committed message remains
authoritative.

`BUZZ_PUSH_ENABLED=false` disables the application producer and workers.
Updated writer connections always bypass any surviving enqueue trigger.
The overlap migration updates an existing function without resurrecting
retired objects. Apply it before relying on isolation with a surviving
trigger, and replace every old enabled process and writer connection:
missing settings preserve legacy behavior during overlap.

SIGTERM/Ctrl-C cancels enqueue, matcher, and delivery work before
listener drain. Durable queues, claims, leases, preferences, and
delivery configuration remain intact. Claims expire normally; gateway
requests already accepted may still deliver. Reactivation requires an
explicit operator decision about retained work. There is no automatic
purge, startup interlock, or backfill of messages written while
disabled.

Built on merged [#8135](#8135),
including [#8178](#8178). Trigger
retirement [#8210](#8210) remains
open; this change is tested with the trigger present and after removal.
Operational details are in [the rollback and reactivation
guide](https://github.com/block/buzz/blob/relay-push-rollback/docs/push-gateway-deployment.md#relay-rollback-and-reactivation).

### Validation


[9d3d710](9d3d710)
changes documentation and Rust comments only, with no executable or
assertion changes. Formatting and diff checks passed;
[12f1d1e](12f1d1e)
additionally restores the reviewer-requested caveat that active lease
renewal may suppress a notification. This is also documentation-only;
Owner approval was confirmed on 12f1d1e.
[a4f602d](a4f602d)
subsequently merges main to resolve a migration-count conflict after
main added migration 0058. Both 0058 and rollback migration 0059 are
retained; the focused embedded-migrator test, formatting, and applicable
desktop pre-push checks passed. Current-head [owner
approval](#8216 (review))
is confirmed. [CI attempt 2
passed](https://github.com/block/buzz/actions/runs/37985516452/attempts/2),
with required checks passing or appropriately skipped. The first attempt
failed only the unchanged replica-floor probe test with `MaskedActivity
{ masked: 1 }`; one failed-jobs retry passed without code changes. All
four push contract tests passed. The current-head [advisory security
review](https://github.com/block/buzz/actions/runs/37985514346/job/114006457769)
has remained in its review step since 20:18:51 UTC without a published
result for over 25 minutes. It is stalled under the advisory-review
policy, not a clean security review.

[Required CI checks passed or were
skipped](https://github.com/block/buzz/actions/runs/37964035783) on
[3164b25](3164b25).
The advisory security review was cancelled without a published result.
Codex's durable-retry suggestion was [rebutted and
resolved](#8216 (comment))
under the explicit best-effort notification contract. The [lease
activation-order
observation](#8216 (comment))
is correct. Under the clarified product requirement, either notification
outcome is acceptable during overlapping registration and message
arrival. Exact commit ordering is not required; deliberate historical
backfill remains prohibited. The bot thread is resolved against that
clarification; [Owner review accepted the clarified overlap
contract](#8216 (review))
on 9d3d710.

All 488 PostgreSQL tests passed. The final four-way producer contracts
passed on desired/migrated schemas, with/without triggers. Added
coverage verifies message commit under push-gate and queue-table locks,
recovery after enqueue failure, in-flight enqueue cancellation, the
lease timestamp filter (not production activation ordering),
serving-lease writers, rollback preservation, reconnects, and
reactivation without backfill. Queue saturation and all three relay
worker shutdown tests passed. Rust lint and all 17 source-policy checks
passed.

Full local CI/repository runs encountered the unchanged ACP
`keepalive_resets_idle_past_deadline` timing failure. Earlier desktop
subprocess timing tests also failed under parallel load and passed as an
isolated module. Under Tom's local pre-push exception, this update
excluded `rust-tests` and `desktop-tauri-checks`; remaining hooks stayed
enabled. Required CI validation remains necessary before merge. A
focused run competing with the full database suite hit wall-clock
deadlines; tests now use a short database lock timeout to distinguish
unwanted push dependencies, and their final isolated run passed.

A local process-replacement rehearsal on 3164b25 used the real relay
binary and a mock gateway holding a delivery request open. SIGTERM
closed that request in under 1 ms; the relay exited in 5.02 seconds.
Restarting the same binary with push disabled produced no further
gateway requests over 35 seconds, beyond the 30-second claim expiry. The
outbox row, lease, and its subscriptions remained byte-for-byte
unchanged. This used a seeded outbox and did not exercise APNs or a
mobile device.

Production writer inventory, shutdown deadline, and retained-queue
disposition still require operational validation before rollout. The PR
is marked ready for review. The overlap behavior is accepted by the
product requirement; owner review accepted that contract. No production
deployment has occurred.

---------

Signed-off-by: Tom Brow <tomb@block.xyz>
* origin/main:
  chore(ci): run Codex security review on gpt-6.1-sol (#8228)
  fix(push): isolate push enqueue and stop workers on rollback (#8216)
  chore(release): release Buzz Desktop version 0.5.28 (#8222)
  feat(relay): reshape read-state API to the sidebar wire format (#8220)
  test(desktop): move CSP guards from Rust to the desktop JS suite (#8172)
  fix(desktop): repair the Windows notification shim's false denial on read (#5600)
  fix(mobile): normalize relay URL before disabling push (#8201)
  feat(buzz-db): run push enqueue and channel TTL refresh in app code (#8135)
  fix(mobile): keep thread content visible while positioning replies (#8134)

Signed-off-by: Honey <8e307ae0076a4dab6b94b036ea3edc7e08f823a625269c1e6919e881a048b4d2@buzz.block.builderlab.xyz>
## Summary

This drops the channel-TTL event trigger. The application already
refreshes ephemeral-channel deadlines in the event transaction
(`event_follow_up::refresh_channel_ttls`, from #8135), so the trigger
only repeats that work.

This PR originally retired both follow-up triggers. #8352 has since
retired the push-match trigger in migration 0063, so after the rebase
this PR covers only the TTL half.

Migration `0065_retire_channel_ttl_trigger.sql`:
- `SET LOCAL lock_timeout = '5s'` (the same bound as 0063)
- drops `events_refresh_channel_ttl` and
`refresh_channel_ttl_after_event_insert()`

Dropping the trigger on the partitioned parent also drops its partition
clones. Published migrations, including 0022 and 0024, stay
checksum-frozen.

The same objects are removed from `schema/` (`schema/functions/…`,
`schema/triggers/events.sql`, `schema/schema.sql`) and from the pgschema
reconcile script. After this, migrated and desired-state databases have
no event follow-up triggers.

Tests:
- `follow_up_retirement_tests.rs` (renamed from
`push_retirement_tests.rs`): the push-retirement upgrade test now stops
at 0063. A new test upgrades 0064 → 0065 and checks that the TTL trigger
is gone from the parent and every partition, that the function is gone,
and that the published checksums haven't changed.
- `event_follow_up_postgres_tests.rs`: the contract now has two arms.
`AppOnly` is the shipped schema, where both triggers are absent. `Dual`
reconstructs the historical overlap of both triggers. The `PushRetired`
arm (the push trigger dropped, the TTL trigger kept) was the shipped
state before this PR. Its tests are removed because `Dual` and `AppOnly`
together cover it.
- `embedded_migrator_contains_consolidated_initial_schema` pins the 0065
statements and checks that both objects are absent from the desired
schema.

**Deploy gate:** do not run 0065 against a database still served by a
relay older than #8135. After 0065, raw SQL writers no longer refresh
TTL deadlines. `docs/push-gateway-deployment.md` is updated to match.

### What got simpler

The trigger and the app no longer both refresh TTL deadlines; the app is
now the only producer. One plpgsql function and one trigger are gone
from both schema paths, and 8 per-partition drops are gone from the
reconcile script. The follow-up contract drops from three arms to two.

### Related issue

BUZZ-313 (Linear), part of the trigger-retirement work.

### Testing

Head is `4f7d0baf0`. Results below are at `678927730` unless noted.
`678927730..4f7d0ba` changes only one test in
`crates/buzz-db/src/store/event.rs`, described in the first bullet.

- **Fixed test,
`permanent_channel_event_commits_do_not_lock_the_channel_row`**
(`4f7d0baf0`).
- **Why it changed:** after 0065, its raw-pool inserts no longer ran any
TTL refresh, so the test passed whatever `refresh_channel_ttls` did.
This was raised in review.
- **What it does now:** it inserts through the production `AdmittedTx`
path and keeps the barrier and the tuple-lock probe. It commits all N
transactions while an external transaction holds `FOR SHARE` on the
channel row. It also asserts that no
`buzz_db_channel_ttl_refresh_failures_total` is counted.
- **Mutation check:** with `SELECT … FOR UPDATE` injected into
`refresh_channel_ttl`, the new test fails (`must not wait on the channel
row`, timeout at 10s). The old test passes under the same mutation.
  - **Blox:** fmt and `buzz-db` clippy pass.

- **GitHub CI at `4f7d0baf0`:** every required check passes (56 pass, 0
fail). CI builds the merge ref with `main` `93ffc37cb`.
- **New and renamed tests, checked by name in the CI logs at
`4f7d0baf0`.** These pass in PostgreSQL Domain / PostgreSQL Tests
([117033725006](https://github.com/block/buzz/actions/runs/38915998692/job/117033725006)):
  - `permanent_channel_event_commits_do_not_lock_the_channel_row`
-
`migration_schema_ttl_retirement_drops_every_partition_trigger_and_keeps_checksums`
-
`migration_schema_push_retirement_preserves_ttl_and_published_checksums`
-
`event_insert_ttl_refresh_handles_permanent_ephemeral_duplicate_and_activation_race`
- `{desired,migration_schema}_event_follow_up_contract_{dual,app_only}`
(four tests)

`embedded_migrator_contains_consolidated_initial_schema` passes in Rust
/ Unit Tests
([117024125423](https://github.com/block/buzz/actions/runs/38915998692/job/117024125423)).
No `*_push_retired` test runs anywhere.
- **Blox gates at `678927730`** (private PG16 + Redis, on a workstation
shared with other sessions):
- `cargo fmt --check`, workspace `clippy -D warnings` and `buzz-db
--lib` all pass.
- The `buzz-admin`, `buzz-audit`, `buzz-deletion`, `buzz-push-gateway`,
`buzz-search` and `buzz-workflow` Postgres packages pass.
- `buzz-db`: 517 of 519 tests passed. The 2 that hung, both
`writer_pool_*` tests, were killed. `buzz-relay`: 413 of 426 passed. The
13 failures are covered below.
- **Uncontended reruns at `4f7d0baf0`** on a fresh, idle workstation
(PG16.15, `competing=0` for every arm):
- **`writer_pool_rejects_non_read_committed_database_default` predates
this PR.** It timed out 3/3 at head and 3/3 at `main` `93ffc37cb`, with
a 300s timeout per run.
- **`writer_pool_metrics_stop_after_session_timeout_setup_failure` also
predates this PR.** It timed out 2/3 at head and 2/3 at `main`, and
passed in the remaining run on each side.
- Both tests pass in CI. The gate accepts them as a named exception for
this PR, as a pre-existing hang on the PG16 test environment.
- **`buzz-db`:** 518 of 519 tests passed. The single failure is
`writer_pool_rejects_non_read_committed_database_default`, killed after
it hung (the exception above).
- **`buzz-relay`: still open.** 413 of 426 tests passed. The same 13
`handlers::group_state_postgres_tests` failed as on the shared box, each
panicking at once in its fixture's `ensure community` step with
`Sqlx(PoolTimedOut)`. Contention does not explain them. The fixture's
community setup is in `buzz-db`, which this PR changes. A head/`main`
comparison of the full `buzz-relay` package on the same idle box is
running to find out whether this predates the PR. All 13 pass in CI at
this head.
- **E2E (Gimli, Blox)** at `050e593af`. `050e593af..6789277` changes
only tests and docs; the migration, schema and runtime code are
byte-identical. Gimli's audited verdict: **EXERCISED AND WORKS**, for DB
and relay runtime only. Gimli ran it at `050e593af`; this head's runtime
is byte-identical but was not freshly executed.
- **Upgrade:** a real relay startup took the schema from 0064 to 0065.
That removed the TTL function and the trigger from the parent table and
from all 8 partitions. Checksums for migrations 1–64 are unchanged.
- **Lock-timeout rollback:** with a real lock held, the migration failed
with `55P03` at 5.0007s and the schema rolled back fully to 64. Once the
lock was released, a retry applied 65.
- **Fresh desired schema:** after pgschema plus reconcile, the retired
objects are absent.
- **Real signed kind-9 sends:** on both schema paths, these refreshed
ephemeral-channel deadlines to about +600s. Permanent channels stayed
NULL.
- **Raw SQL insert:** at 64 it refreshed the deadline. After 65 it left
the deadline unchanged, on both the upgraded and the fresh schema.
  - **Not covered:** native or device testing, and deploy.
- **Review:** Legolas found 0 P0 and 0 P1. His three optional P2s are
fixed in `678927730`.
- **No human app test:** this is a DB-only change.
- **Migration numbering:** #8237 and #8372 also add a `0065_*`
migration. Whichever PR merges second must renumber.

---------

Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Co-authored-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>


* fix(chart): own the Datadog version label on every workload Pod (#7876)
## Summary
Every chart-managed Pod now carries a chart-owned
`tags.datadoghq.com/version` label derived from the deployed image,
instead of a value each wrapper restates once per workload.
Covered Pod templates:
- relay Deployment (`templates/deployment.yaml`)
- pairing relay (`templates/pairing-relay.yaml`)
- storage-accounting CronJob
(`templates/storage-accounting-cronjob.yaml`)
- operator jobs, including the deletion drain
(`templates/_operator-jobs.tpl`)
**Source order:** `image.tag`, then `image.digest`, then
`Chart.AppVersion` (`buzz.imageVersionSource`). Tag-first is deliberate:
- The rendered value matches the `sha-<commit>` pins wrappers already
carry, so upgrading to this chart does not roll any Pods.
- An image promotion only has to write `image.tag` + `image.digest`. No
per-workload label edit is needed.
Exact runtime identity stays exact in two places. The image reference is
`repository@digest` when a digest is pinned.
`BUZZ_STORAGE_SNAPSHOT_CODE_SHA` (persisted as `code_sha`) is still
digest-first.
**Label safety:** `buzz.imageVersionLabel` maps any OCI tag or digest to
a valid label value.
- Valid values already in Datadog's normal form (lowercase, no `__`)
pass through byte for byte, so `sha-<hex>` and `1.2.3-rc.4` are
unchanged. Datadog lowercases tag values and collapses `__`, so any
other value is hashed rather than allowed to report the same version as
a different revision.
- A digest keeps 63 hex characters.
- Anything else is replaced by the first 63 hex characters of its
SHA-256.
- Exactly 63 lowercase hex characters is reserved for the hashed and
digest forms, so a rendered label cannot be fed back as a tag to make
two revisions collide.
- When both tag and digest are set, the label names the tag even if they
disagree; the digest still pins what runs.
**Precedence:** a `tags.datadoghq.com/version` supplied through any
workload's `podLabels` is ignored. Every other label, including
`tags.datadoghq.com/env` and `/service`, passes through unchanged.
Overriding instead of failing means a wrapper with a stale pin is
corrected by the upgrade itself. The chart bump and the wrapper cleanup
don't have to land together.
**What got simpler:** one image identity instead of N. Wrappers delete
their per-workload version pins. Image promotion tooling no longer needs
a "mirror the tag into a label path" feature. One shared helper
(`buzz.podLabelsWithVersion`) replaces four `podLabels` passthroughs.
Chart `0.1.10 → 0.1.11`, with an `artifacthub.io/changes` entry.
Documented in the chart README ("Datadog version label") and
`docs/deployment-identity.md`.
Note: a vendor-namespaced label now renders unconditionally in an OSS
chart. This is in tension with
[VISION_SOVEREIGN.md](../blob/main/VISION_SOVEREIGN.md). The label is
inert without the operator-supplied `tags.datadoghq.com/service`/`env`,
and the chart already ships vendor-specific defaults (e.g.
`sidecar.istio.io/inject`).
### Testing
Run on a Blox (Linux) workstation at tree `41634b7ca` (helm v3.16.4,
helm-unittest 0.8.2, the CI versions):
- `helm lint deploy/charts/buzz`: 0 failed
- `helm unittest deploy/charts/buzz`: 12 suites, **85/85 passed**
New `tests/version_label_test.yaml` checks the relay, pairing relay, and
deletion drain: tag wins over a stale `podLabels` pin, the label is
stamped with no `podLabels`, and digest-only images get a label-safe
value. `tests/storage_accounting_test.yaml` covers the same cases for
the CronJob, plus the `Chart.AppVersion` fallback.
Mutation checks:
- Reverting any one template to the plain `podLabels` passthrough fails
tests.
- Switching the source order to digest-first fails tests.
- Restoring the case-insensitive passthrough fails the three
Datadog-normalization tests (uppercase, `__`, uppercased 63-hex).
No Rust, desktop, web, or mobile sources changed.
## Linear tracking
Related work: [BUZZ-215](https://linear.app/squareup/issue/BUZZ-215).
---------
Signed-off-by: tornquist <tornquist@squareup.com>
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Co-authored-by: Claude Opus 5 <noreply@anthropic.com>
Co-authored-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
* feat(db): advance an empty partition catch-all under bounded locks (#7993)
## Summary
Adds bounded, serialized advancement of an empty right-edge partition
catch-all for `events` and `delivery_log`. The repaired catalogs
currently end in an empty catch-all from 2027-01-01, and the merged
manager (#6515) only audits them. Without this change, January writes
land in the catch-all, after which only an operator can move them.
When `BUZZ_PARTITION_MANAGER_ADVANCE_ENABLED=true`, each relay keeps six
dedicated monthlies after the current month. It does this at startup and
on every audit interval by replacing the empty catch-all with canonical
monthlies and a new canonical `<table>_p_future` after the horizon. From
today's catalogs the first run creates January–March 2027 and moves the
catch-all to April 2027.
## Safety design
- **Refuse before locking.** The following return `operator_required`
without taking any table lock:
- a populated catch-all, or one whose occupancy is unknown;
- a catch-all with child-only triggers, which the replacements would not
inherit;
- a misaligned bound;
- a `DEFAULT`, anomalous or pending-detach child;
- a name collision.
- **One winner.** A schema-scoped `pg_try_advisory_xact_lock` is taken
before any DDL. Losers report `skipped_locked` and never issue DDL. The
winner re-plans from a fresh audit before taking any table lock and
checks for collisions. A runner that lost a race therefore sees the
committed layout as a no-op, not as colliding names.
- **Writer lock order.** First `ONLY` the parent is locked `ACCESS
EXCLUSIVE` under a 2 s `lock_timeout`. Then each foreign-key counterpart
(today only `communities`) is locked in OID order `SHARE ROW EXCLUSIVE
NOWAIT`, then the catch-all `NOWAIT`.
- The counterparts are read again once the parent is locked, and that
set is the one locked. Any FK DDL on or to the parent conflicts with the
parent lock, so the set can't change after that. An FK committed while
maintenance waited is therefore locked `NOWAIT` too, so attaching never
waits on it under the parent lock. The read before the lock remains as a
cheap early refusal.
- This is the order an insert takes locks (parent, then the FK check on
`communities`), so maintenance cannot deadlock with ingest. The internal
manual runbook used to lock `communities` first; it now uses this order
too.
- `SHARE ROW EXCLUSIVE` is the strongest lock the DDL takes on
`communities`; measured on PG 16 and 17, the catch-all `DROP` takes
none, as long as the catch-all's only foreign keys are those inherited
from the parent. A catch-all with its own foreign key, or one that
another table's foreign key references, is refused: once before any
lock, and again after the catch-all lock, where the check is
authoritative. Readers and other writers' `FOR KEY SHARE` checks
proceed. A concurrent `communities` writer makes the run fail fast with
`lock_timeout`.
- A `40P01` deadlock victim is also reported as `lock_timeout`.
- Parents that are referenced by a foreign key, or that reference an
inherited table, are refused, including when such a key commits while
maintenance waits on the parent.
- **Re-plan under lock.** The catalog is re-audited under those locks.
The transaction proceeds only if the plan is unchanged.
- **Bounded.** `statement_timeout` 5 s,
`idle_in_transaction_session_timeout` 5 s, and a 10 s client deadline
per table. A deadline-abandoned connection is closed, never returned to
the pool, and the server rolls back anything uncommitted. If the
deadline fires after `COMMIT` was sent, the change may have landed; the
next audit reports the truth. The orphaned backend keeps its locks until
its in-flight statement ends, at most `statement_timeout`.
- **Verify before commit.** The changed catalog is re-audited inside the
transaction for bounds, canonical kinds, trigger parity and catch-all
emptiness, and serving safety must not regress. It also checks that
every new child has valid, ready clones of each parent index and
validated clones of each PK/unique/FK constraint.
- **Audits tolerate a concurrent advance.** Catalog rows come from the
statement snapshot, but `pg_get_expr` renders from current catalog
state. So an audit that overlaps another relay's `DROP` of a catch-all
can see a partition that no longer exists. The read-only audit detects
this (a NULL bound, or `42P01` from the emptiness probe) and retries up
to twice with a fresh snapshot.
- **Fail fast on audit probes.** If another relay's audit is probing the
catch-all's emptiness, the catch-all `NOWAIT` lock fails and the run
reports `lock_timeout`. The parent lock is then released immediately,
and the next runner or interval completes the advance.
Uncovered-month creation (`BUZZ_PARTITION_MANAGER_CREATE_ENABLED`,
default `true`) now runs through the same locked transaction, replacing
the unlocked per-month `CREATE`. That flag remains the kill switch for
all automatic partition DDL: with it off, advancement is disabled too.
With advancement disabled (the default) the periodic loop stays
read-only and startup behaves as before, apart from the locking.
A runner that planned DDL always re-audits before returning, even when a
peer did the work, so it never reports the pre-maintenance layout. A
serialized re-plan that finds only disabled work reports
`skipped_disabled`.
## Behavior changes
- The relay audit horizon and the `buzz-admin partition-audit` default
are now 6 months (`PARTITION_MANAGER_MONTHS_AHEAD`), up from 3. Until
advancement is enabled, months already covered by the catch-all make
`degraded` true. That correctly reports a runway under six months.
- New metric `buzz_partition_maintenance_runs_total{table,outcome}` with
outcomes `noop | skipped_disabled | created | advanced | skipped_locked
| operator_required | lock_timeout | deadline | error`.
`buzz_partition_create_attempts_total` keeps its per-month `created |
skipped_covered | error` labels. `error` there still means a DDL or
collision failure; `lock_timeout` and `deadline` runs add nothing to it,
and only `buzz_partition_maintenance_runs_total` records them.
- `ensure_future_partitions` (free function and `Db` method) is removed;
`maintain_partitions` is the one entry point.
- New advisory-lock label `lock_type="partition_maintenance"`.
## Rollout
Enable `BUZZ_PARTITION_MANAGER_ADVANCE_ENABLED` per environment in BPCI:
`bb-block-staging` first, then production. The staging canary proves a
real advance because the six-month horizon already extends past January.
Fallback: rerun the internal manual runbook, which uses the same
parent-first lock order as of 2026-10-05. It keeps `ACCESS EXCLUSIVE` on
the counterparts, because its detach/attach can drop FK triggers on
them.
## Testing
- `cargo test -p buzz-db --lib partition`: 17 unit tests. The 10 new
ones cover:
- plans: repaired layout, policy gating, no-op, refusal states including
child-only triggers, December→January;
- the create kill switch also stopping advancement;
- the month cap at exactly 120;
- per-month metric outcomes for transient failures versus DDL failures;
- the mid-audit-drop retry classifier.
- `cargo test -p buzz-db --lib partition -- --ignored` (PostgreSQL 17):
48/48 on 9 consecutive runs, including 17 new tests:
- advance to the canonical layout, with routing and idempotent rerun;
- replacing a canonically named catch-all in one transaction;
- populated catch-all refused in under 1 s while the parent is locked;
- a `communities` writer making the run fail fast and roll back;
- a `communities` reader not blocking the advance;
- an in-flight insert's FK check, and its write to `communities`, behind
queued maintenance completing without a deadlock;
- a foreign key committed while maintenance waits on the parent, with a
writer on its new counterpart, failing fast as `lock_timeout` on that
table instead of waiting under the parent lock;
- a foreign key referencing `events`, committed while maintenance waits
on the parent, being refused under the parent lock;
- a catch-all's own foreign key, or a foreign key referencing it, being
refused before the parent lock with the key intact, and a catch-all key
committed while maintenance waits on the parent being refused after the
catch-all lock;
- a `40P01` deadlock victim being classified as `lock_timeout`;
- parent contention timing out without blocking the other table;
- held advisory lock skipping with no DDL;
- concurrent runners converging, with at most a transient
`lock_timeout`;
- a stale audit after a concurrent advance being a no-op, and the losing
runner returning the committed layout;
- a re-plan that finds only disabled work reporting `skipped_disabled`;
- an audit retrying when a listed partition is dropped mid-audit;
- a catch-all with a child-only trigger being refused;
- client deadline abandoning the attempt and closing the session (scoped
to the test's own blocked backend);
- catch-all name collision;
- incoming foreign key refused.
- Mutation checks:
- restoring the old counterpart-first `ACCESS EXCLUSIVE` order fails the
reader test (`lock_timeout`) and the writer test (a ~1 s deadlock wait);
- dropping `NOWAIT` from the counterpart lock, or allowing a populated
catch-all, fails the matching tests;
- removing the parent-locked counterpart re-read fails the committed-FK
tests (the parent is held 2.06 s waiting on the new counterpart), and
ignoring its refusal fails the referencing-FK test;
- locking the counterparts `SHARE ROW EXCLUSIVE` before the parent fails
the writer test;
- removing either catch-all foreign-key check fails its test.
- Full PostgreSQL lane: 716/718. Both failures are timing-sensitive
tests outside partition code, and each passes 3/3 when run alone:
- `hanging_redis_peer_times_out_before_the_health_listener_binds`;
-
`readiness_check_cancellation_balances_waiter_and_inflight_connection`.
- `cargo clippy -p buzz-db -p buzz-relay -p buzz-admin --all-targets -D
warnings` and `cargo fmt --check` are clean.
## Related
Refs #2396.
This PR conflicts textually with #7994 (partition audit observability
follow-ups) in `crates/buzz-db/src/store/partition.rs` and
`crates/buzz-relay/src/main.rs`. Whichever PR merges second will be
rebased onto the other.
🤖 Generated with [Claude Code](https://claude.com/claude-code)
---------
Signed-off-by: Ian Oberst <ioberst@block.xyz>
Co-authored-by: Ian Oberst <ioberst@block.xyz>
Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>
* feat: raise hosted community limit to fifty (#8186)
## Summary
- Raise the stock relay active ownership quota from 5 to 50 for creation
and ownership transfer. Raise the absolute lifetime quota from 20 to 50
reserved hosts; completed owner deletions still permanently consume
lifetime capacity to bound create/delete host squatting.
- Honor the owner-list `can_create` projection across Desktop settings,
create flow, and onboarding instead of imposing a client-side count.
Display server `quota_used` / `quota_limit` when available; when the
projection is missing, let the server's `limit_reached` decide.
- Cover 49→50 and 50→51 admissions, deleted-owner lifetime exhaustion,
and rendered create gates under 5/50, 0/50 exhausted, and missing
projections.
## Verification
- Desktop full `pnpm test` and `pnpm typecheck` pass after the 50-cap
update; `cargo fmt --all -- --check` passes. Four targeted Playwright
cases and `pnpm build:e2e` passed for the original dynamic-quota change
at the previous commit, before changing test fixtures from 20 to 50.
- `cargo test -p buzz-db --lib` cannot compile here: macOS dyld rejects
the `sqlx_macros` dylib with `mis-aligned LINKEDIT string pool` on this
host before the crate's tests run. CI must validate the DB package.
## Rollout / manual validation
- Confirm `BUZZ_MAX_COMMUNITIES_PER_OWNER` is unset or 50 on **every**
production relay replica; this per-process cached override takes
precedence over the stock default.
- Confirm Builderlab's list/create/transfer proxy passes the relay's
`quota_used`, `quota_limit`, `can_create`, and `limit_reached` without
its own 5-community gate. Its backing implementation is not in this repo
and was not verified here.
- Human test: with an owner at 49 live communities, create the fiftieth,
verify the fifty-first returns `limit_reached`; transfer into an owner
at 49 then at 50 and confirm the same boundary. Check a deleted-owner
account at 0 active/50 lifetime displays the generic limit and disables
creation. This manual check remains outstanding.
---------
Signed-off-by: am <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@buzz.block.builderlab.xyz>
Co-authored-by: am <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@buzz.block.builderlab.xyz>
* docs(nip-ap): add teams and kind:44300 instructions versions (#8191)
🤖 This PR adds two things to NIP-AP: a Teams section, and `kind:44300`
instructions versions, an owner-private history of each agent's and each
team's instructions. Today instructions are edited in place, so there's
no way to see past edits, tie a behavior change to an edit, or roll
back.
**Teams.** A team is identified by owner, community, and team id, using
the same id grammar as the `kind:30178` `d` tag. The section defines
what membership means (scoped by owner and community, not channel
membership, follows the team's current instructions), how team
instructions combine with an agent's own at launch, and the existing
rule that an agent in several teams can't start if their instructions
differ. How a client stores its private team records stays
client-defined, so this doesn't standardize discovering another client's
private teams.
**`kind:44300`.** A regular event, so every save is a new event and a
subject's events are its history. Each event names exactly one subject:
an agent (`p`) or a team (`t`). Content is NIP-44 encrypted to the owner
as `v1:` plus the raw text, which keeps empty text representable and
caps `content` at 218,548 bytes for the 128 KiB text limit. Current is
the newest version, and history pages with the `until` + `before_id`
cursor so versions saved in the same second are never skipped. Restore
and Reset to template append a new version. Launch order for an agent's
own instructions is its current version, then the linked `30175` prompt,
then a definition-less `30177`. The relay keeps it author-only on every
read surface, excludes it from search, and applies the subject filter
before `LIMIT`. Deletion requests for these versions must carry `["k",
"44300"]` and get the same author-only treatment, since they reveal
version ids and deletion times. A `30178` share is a snapshot: saving a
version doesn't change an existing share.
**Changes to existing spec text:**
- Removed the sentence saying `kind:30176`'s body is untouched "so
device sync keeps its contract". The current desktop client doesn't sync
teams through `30176`.
- Reworded the `30178` `d` tag rationale so it no longer refers to a
`30176` head.
- The "30175 beats 30177" rule now says a current `44300` version beats
both for an agent's instructions.
- Replaced the stale search bullet. It claimed no shared-gated kind is
in an FTS allowlist; search indexes those kinds, and each result passes
the per-event visibility check before delivery.
Relay and desktop implementation follow in separate PRs once this is
approved.
---------
Signed-off-by: Will Pfleger <pfleger.will@gmail.com>
Signed-off-by: Paul <4a1bfa0013bc6d14a8d600d8bf6392efefbd2a26ac3c96c9b2a106b0d12297ca@buzz.block.builderlab.xyz>
Co-authored-by: Paul <4a1bfa0013bc6d14a8d600d8bf6392efefbd2a26ac3c96c9b2a106b0d12297ca@buzz.block.builderlab.xyz>
* fix(push): stop backfilling messages on lease activation (#8178)
Remove the 120-second message scan from push lease activation and
renewal. Subsequent eligible messages continue through the existing
database trigger. The lease protocol, schema, trigger, and advisory-lock
order remain unchanged.
Related enqueue-gating work: #2145. No duplicate open PR or issue found.
### Validation
- All 18 PostgreSQL push persistence tests pass against isolated
desired-state databases after review changes.
- The existing concurrency test verifies activation waits for an
in-flight insert and a subsequent message queues once. The retention
fixture activates its lease before inserting its message.
- Formatting and PostgreSQL test discovery pass. The earlier full local
run passed repository lint/static checks, native desktop pre-push
checks, and every non-ACP integration step.
- Broad local checks hit unrelated ACP idle/keepalive timing failures. A
serial retry passed two affected tests but still failed the keepalive
deadline test. The pre-push hook was skipped with author authorization
after its other checks passed.
---------
Signed-off-by: Tom Brow <tomb@block.xyz>
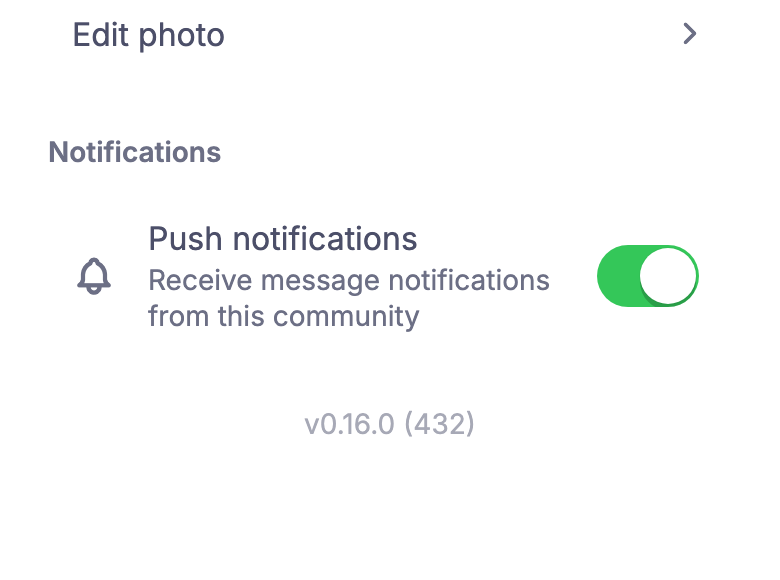
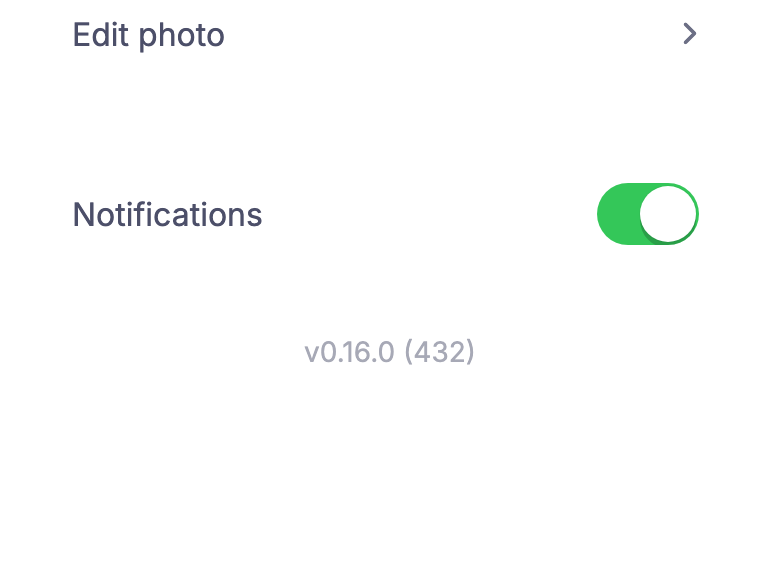
* fix(mobile): simplify notification settings (#8199)
Keep notification settings as a separate card with a single
“Notifications” toggle. Remove the section heading, bell, all subtitles
(including permission/capability and pending opt-out messages), and the
iOS settings button.
Toggle callbacks, capability visibility, persisted opt-in/out, and relay
synchronization are unchanged. The disable failure is being investigated
separately. This intentionally removes the pending warning rather than
claiming to fix synchronization. Tom explicitly requested removal of the
immediate opt-out synchronization warning and all other status text;
this is an intentional exception to the pending-feedback guidance in
VISION_MOBILE.md. [Codex’s finding is answered against that agreed
scope](https://github.com/block/buzz/pull/8199#discussion_r4225426842).
No new tests. Delete tests for the removed permission/settings UI and
remove obsolete display assertions from existing recovery tests while
preserving their opt-out synchronization coverage.
Closest related issue:
[#7826](https://github.com/block/buzz/issues/7826). No duplicate cleanup
PR found.
### Validation
Mobile formatting/static analysis passed. The full existing mobile suite
passed (3,216 tests; 4 skipped), plus the three unconfigured-build tests
and gateway recipe checks. Existing opt-out recovery tests exercised the
switch, persisted tombstone, snapshot synchronization, and successful
relay retry.
Before/after renders use the existing Flutter widget fixture with
synthetic data and mocked native navigation. No simulator or TestFlight
run was performed. After merge, validate the settings row and on/off
flow in the next iOS candidate; remote disable failure remains a
separate investigation.
GitHub CI also passed the mobile tests, unconfigured-build tests, and
gateway recipe checks. The [security
review](https://github.com/block/buzz/actions/runs/37863885299)
completed successfully. The [Android
build](https://github.com/block/buzz/actions/runs/37863554077/job/113605025305)
passed. The iOS simulator build, native accessibility checks, and
unsigned iOS release build passed. [All required CI
checks](https://github.com/block/buzz/actions/runs/37863554077) are
green.
### Before and after
Headless Flutter widget fixture, with synthetic data and mocked native
navigation.
| Before | After |
| --- | --- |
| 
| 
|
Signed-off-by: Tom Brow <tomb@block.xyz>
* fix(mobile): keep thread content visible while positioning replies (#8134)
Opening a mobile thread could blank the original message while the app
positioned replies. This affected empty and populated threads, including
links to a specific reply.
Keep one original-message widget mounted and usable throughout
positioning. It follows a measured placeholder in the reply list, which
becomes visible only at its final position. This preserves media and
reaction ownership, supports scrolling through tall originals, and
excludes the head from input and accessibility when it leaves the
viewport.
### Validation
- Added production-path frame regressions for empty, short, long, and
deep-linked threads; two video lifecycle cases verify exactly one
initialization and disposal, including completion after navigation away.
- Added coverage for dragging, mouse-wheel and accessibility scrolling,
removal of offscreen and app-bar-covered head semantics, and scrolling
to the interactive bottom of a 70-line original message. Removing the
accessibility exclusion or restoring the raw viewport-top boundary fails
both long-thread regressions; restoring the duplicated head fails the
lifecycle test.
- Mobile dependency setup, analysis, the full mobile test suite, and
unconfigured-push tests passed. The native iOS simulator debug build
passed after integrating main, including the conflict resolution for the
new Buzz icon API. The current tree passed 3,076 mobile tests (four
skipped) and three unconfigured-push tests, and the updated native
simulator build passed.
- Exercised empty, three-reply, forty-reply, and older-reply deep-link
flows on an iPhone 17 Pro simulator against an isolated local relay with
a disposable identity. Confirmed correct head accessibility coordinates
and absence when offscreen. The local posterless-video fixture rendered
its attachment fallback; native decoding success is not claimed.
Resource ownership is covered through the production preview-loader
seam. [Updated simulator
captures](https://github.com/block/buzz/pull/8134#issuecomment-6047098230).
- Added delayed-hydration regressions for mouse-wheel and explicit
accessibility scrolling through the persistent head. Both preserve a
visible reading anchor across hydration and viewport resizing; removing
the user-scroll lifecycle callbacks makes both fail. Repeated empty,
populated, and older-reply deep-link opening with the updated native
build against the retained isolated relay.
- Entered and sent a reply from the disposable simulator identity
against the isolated local relay. The app displayed the reply and
cleared the composer, and the relay database confirmed persistence.
Software keyboard open/close remains unverified because the simulator
did not display it.
- Agent review feedback was addressed. Personal mobile testing is not
applicable under the author's standing exception.
Post-merge validation: repeat empty, populated, and deep-linked thread
opening in the integrated mobile candidate, including keyboard
open/close and sending a reply before release.
buzz-review-completed
---------
Signed-off-by: Tom Brow <tomb@block.xyz>
* feat(buzz-db): run push enqueue and channel TTL refresh in app code (#8135)
## Summary
Moves the producer side of the two event follow-up triggers into
application code. The triggers stay in place, so both producers run
until a later change drops the triggers after this ships to every pod.
Builds on #8130 (`AdmittedTx`). Refs BUZZ-176.
### Push match enqueue
New `store::event_follow_up::enqueue_push_match` replaces the
`events_enqueue_push_match` trigger
(`schema/functions/enqueue_push_match_job.sql`, migration 0023) and
matches it exactly:
- Same kind allowlist (9, 40002, 45001, 45003), now `PUSH_MATCH_KINDS`.
- Takes the same SHARED `buzz_push_gate:<community>` advisory lock as
its own statement, so under READ COMMITTED the lease check gets a
snapshot taken after the lock is granted. Lease activations still take
it EXCLUSIVE in `push.rs`.
- Same lease predicate (`active AND endpoint_enabled AND expires_at >
now`), then `INSERT push_match_queue ... ON CONFLICT DO NOTHING`.
- Fails closed: any error rejects the event, as the trigger did.
It runs right after the INSERT, only when the insert affected a row. The
consumer side (claims, `lease_until`, attempts, reaper) is already
app-owned and is unchanged.
### Channel TTL refresh
`AdmittedTx` now records every channel that received an event (except
kind 9007 and channel-less events). `AdmittedTx::commit()` refreshes
their `ttl_deadline` as the last statement before COMMIT, which keeps
the commit-time behavior of the deferred `events_refresh_channel_ttl`
trigger (migration 0024):
- One savepoint per channel, in sorted order, under the same SHARED
`buzz_channel_ttl:<community>:<channel>` lock.
- Runs the same `UPDATE` with the same `archived_at`/`deleted_at`
filters as its own statement after the lock, so its snapshot follows the
lock grant. Its `ttl_seconds IS NOT NULL` qual filters a permanent
channel before any tuple lock, so a permanent channel's row is never
locked. An ephemeral channel's row lock is held through the remaining
refreshes and the COMMIT round trip (the trigger held it only inside
COMMIT).
- Lock keys come from one builder per protocol
(`channel::channel_ttl_lock_key`, `push::push_gate_lock_key`), shared by
the SHARED and EXCLUSIVE sides. The shared push-gate wait is observed
through `observe_advisory_lock(LockType::PushGate, …)`.
- On failure it rolls back the savepoint, logs a warning, and increments
`buzz_db_channel_ttl_refresh_failures_total{reason}`, where `reason` is
`lock_timeout` or `error`. The event still commits, matching the
trigger's `EXCEPTION WHEN OTHERS`. A cancelled statement (`57014`) still
rejects the transaction, because plpgsql never caught that either.
- While both producers run, an app refresh that hits `lock_timeout` is
counted, and then the trigger retries it inside COMMIT and may succeed.
So during the dual window the failure counter can over-report and the
worst-case wait doubles. Both go away when the retirement PR drops the
triggers, after which the counter is exact.
### Call sites
Every production `INSERT INTO events` calls
`event_follow_up::after_admitted_insert`:
- `insert_event_on`
- `insert_event_with_thread_metadata_tx`
- `LockedMemberSnapshot::replace_member_event`
- `replace_addressable_event`
- `publish_nip43_membership_locked`
- `accept_lease_event` (kind 30350, a no-op today, kept so the policy
has no exceptions)
`replace_parameterized_event_in_transaction_impl` inserts inside the
`parameterized_replace` savepoint. It enqueues the push job inside the
savepoint, so a rollback to that savepoint also drops the job, and
records the TTL channel only after the savepoint is released.
The two rolled-back verification probes (`verify_floor_guard_behavior`,
`verify_channel_roster_fence_behavior`) are named exceptions, because
they never commit.
### Source policy
`tests/observability_source.rs` adds
`every_production_event_insert_runs_the_follow_up_hook`. It scans every
`crates/*/src` and fails on any function that inserts into `events`
without the hook. Matching is normalized (letter case, whitespace, `\`
continuations, `\n`/`\t`/`\r` escapes, optional `public.`). The file is
masked once first: comments (`//`, nested `/* */`) and string,
raw-string (including `br"`/`cr"`), and char literals become spaces.
`#[cfg(test)]` markers, `fn` signatures and the hook are all found in
that masked view, so a marker in a comment (even a multiline block
comment) strips nothing, an `fn` line inside a multiline string doesn't
split a function, and a commented-out or quoted hook doesn't count. SQL
is still matched in the original text. A table test pins the masker's
output for each literal form. A fixture test pins what the scan rejects
(no hook, push without TTL, a hook in a line comment, block comment, or
string, lowercase or line-broken or escaped SQL, writers after test-only
items or under comment mentions) and what it ignores (writers in
`#[cfg(test)] mod`). A floor of seven hooked writers catches a scan that
silently stops seeing writers.
### Tests
`src/store/event_follow_up_postgres_tests.rs` is the contract suite from
the BUZZ-176 discovery work, ported to the `AdmittedTx` API. It is a
crate-internal `#[cfg(test)]` module because it runs `SET LOCAL`
timeouts and in-transaction reads through the crate-private
`AdmittedTx::conn()`. It runs on both the desired and migration schemas,
in two arms:
- **dual**: production during the migration window, with the triggers
and the app code both running.
- **app-only**: drops both triggers in the disposable database (and
asserts no partition clones remain), the way the retirement migration
will.
The trigger-only baseline is the base branch, where the same suite
passed before this change. The suite also pins the two branches that
differ from "swallow everything": a `lock_timeout` failure increments
`buzz_db_channel_ttl_refresh_failures_total{reason="lock_timeout"}`
exactly once, and a statement cancel (`57014`) during the refresh
rejects the event with no row, job, or deadline change.
## What got simpler
Nothing yet. This adds a parallel producer during the migration window.
It is what lets the follow-up PR delete two plpgsql functions, two
triggers, and the "keep in sync with migrations/00xx" duplication
between `schema/functions/` and `push.rs`.
## Verification
Rebased onto `main` @ `745501962`. All runs used a Linux cloud
workstation with the pinned toolchain (rustc/clippy 1.95.0, hermit), and
the tree was clean before and after each run. The final head,
`c5a06a82`, changes only `crates/buzz-db/tests/observability_source.rs`
compared with `1eb11bde` (via `fbc9a598`, `7c0baa41`, `9199992c` and
`d405b2f6`). Production source is identical between the two.
| Check | SHA | Result |
|---|---|---|
| `cargo fmt --check`, `cargo clippy -p buzz-db --all-targets -D
warnings` | `fbc9a598` | pass |
| `cargo clippy` (workspace) | `1eb11bde` | pass |
| source policy (`--test observability_source`), fmt, buzz-db clippy |
`c5a06a82` | 17/17, pass, pass |
| `cargo test --locked -p buzz-db` (non-PG) | `c5a06a82` | 148 lib + 17
policy + 5 doctests |
| source policy (`--test observability_source`) | `fbc9a598` | 16/16 |
| `cargo test --locked -p buzz-db` (non-PG) | `fbc9a598` | 148 lib + 16
policy + 5 doctests |
| contract suite (`store::event_follow_up_postgres_tests`,
desired/migration × dual/app-only) | `1eb11bde` | 4/4 |
| buzz-db PG full | `1eb11bde` | 464/464 |
| buzz-relay PG | `1eb11bde` | 378/378 |
| GitHub CI | `fbc9a598` | 53 pass, 0 fail (Codex security review
pending) |
**Falsifications** (each mutation made the named test fail, then was
reverted):
- dropping the `relay_members` hook → policy names
`publish_nip43_membership_locked`
- no-op push producer → app-only arms fail, dual arms pass (trigger
covers)
- skipping the TTL refresh → app-only fails on the deadline; dual fails
on the failure-metric assertion
- swallowing `57014` → all four arms fail
- dropping the metric increment → all four arms fail
- unanchored `#[cfg(test)]` match, or no escape handling → fixture test
fails
- a `#[cfg(test)]` constructor that skips admission, added inside `impl
AdmittedTx` (indented or as a column-0 `mod`) →
`admitted_tx_is_constructed_only_by_admitting_constructors` fails;
putting the strip back into the constructor scan → its fixture test
fails
- at `7c0baa41`: `accept_lease_event`'s hook commented out and the real
call made through an alias → policy names `accept_lease_event` (the same
mutation passes under the `fbc9a598` policy); hook matching on unmasked
text → the comment/string fixtures fail
- at `9199992c`/`d405b2f6`: no nested block-comment depth, no
string-escape skip, no `br"`/`cr"` raw-literal prefix, or no raw-string
branch at all in the masker → the follow-up fixture test fails
- at `c5a06a82`: finding `#[cfg(test)]` in the unmasked text →
`writer_after_block_commented_cfg_test` is no longer reported; finding
`fn` signatures in the unmasked text → `writer_after_raw_string_example`
is no longer reported; no `cr` raw prefix → the masker table test fails
on `cr"`
- unhooked writers appended to `side_effects.rs` (after test-only items,
under a doc-comment mention, with an escaped newline) → policy names
each
**Live relay E2E**: an independent reviewer ran this at `1eb11bde`
against a real relay and CLI, with PostgreSQL 17 and Redis 7, the
follow-up triggers absent, and no partition clones.
- A kind 9 on a TTL channel advanced the shortened deadline by about 580
s. On a permanent channel, the deadline stayed NULL.
- Each accepted event produced exactly one pending `push_match_queue`
row with the same event id.
- An exact signed replay was a no-op.
- While the exclusive TTL lock was held, the event and its job stayed
invisible and the deadline didn't change. After release, both persisted
once.
- Roster create/join/add/remove kept SQL and wire state in step
(1→2→3→2), with one current 39002 head.
- NIP-33 replace, duplicate, stale, failure and retry cases all passed.
Limits: the push lease was a SQL fixture, and push consumers were
disabled. Kind 30023 is global, so channel-scoped TTL on the
parameterized path is covered only by the PG contracts. No live relay
rerun was done at `fbc9a598`, because that delta is test-only.
**Latency** (measured at pre-rebase `f8380927`, same production delta;
debug build on loopback, 1,000 samples per cell, EVENT→OK): head
app-only p50/p99 3.80/4.58 ms (permanent) and 3.87/4.64 ms (TTL),
against base trigger-only 3.49–3.53/4.00–4.03 ms and 3.56–3.62/4.30–4.46
ms. About +0.3 ms p50, from the extra client round trips (lock, UPDATE,
savepoints, push lock/insert) that the triggers ran server-side. One
debug loopback run, not a production p99.
Not measured: contention from many writers on one hot TTL channel, where
each writer now waits on the channel row lock for about two more client
round trips (RELEASE SAVEPOINT and COMMIT) than with the trigger. In
review, a burst of 8 concurrent posts to one TTL channel committed with
no deadlock or lock timeout. Watch send p99 and `pg_locks` waits on
`channels` during rollout.
**Known pre-existing, not touched here:**
`api::mesh_demo::tests::demo_join_forwarded_arm_round_trips_echo` is
flaky when Redis is present. It returns a 504 in 4 of 5 runs at base
`745501962` and 2 of 5 at `fbc9a598`, always at the same assertion. No
CI lane selects it.
---------
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Co-authored-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
* fix(mobile): normalize relay URL before disabling push (#8201)
Communities joined with a `ws://` or `wss://` relay URL cannot disable
push: the opt-out path passes that URL directly to the HTTP-only NIP-11
fetcher, fails before publishing the inactive lease, and leaves the
durable retry pending. This was reproduced in USB logs from TestFlight
0.20.1 (49).
Normalize the URL with the existing push relay HTTP helper before
fetching metadata, matching the revocation outbox's handling. No
settings UI changes. Related: #8199 removes the status text but does not
fix this synchronization failure; no duplicate fix found.
### Validation
Four regression cases exercise the real community deactivator through
its HTTP boundary. The WebSocket cases fail with the device's exact
exception before the fix; all four pass afterward. All 37 focused
community/revocation tests and targeted Flutter analysis pass. An
initial full mobile run had three failures (recount timing and native
export timeout/order); all three passed in isolated reruns. The full
mobile checks and test suite passed on retry. The local repository-wide
gate stopped during Rust compilation without a final result; a full
local pass is not claimed. [GitHub
CI](https://github.com/block/buzz/actions/runs/37865048873) passed,
including mobile tests, Android build, Swift tests, iOS simulator build,
and unsigned iOS release build. [Codex
review](https://github.com/block/buzz/pull/8201#issuecomment-6071795750)
reported no major issues.
The installed TestFlight build is unchanged. After this fix lands,
validate that upgrading the same installation clears its existing
pending opt-out and leaves the relay lease inactive, without toggling
notifications back on.
Signed-off-by: Tom Brow <tomb@block.xyz>
* fix(desktop): repair the Windows notification shim's false denial on read (#5600)
Addresses #2445. Closely related to #2483 -- see "Relationship to #2483"
below; I am happy to close this in favour of that one.
## The problem
On Windows the notification plugin's injected shim decides its
permission at startup like this
([`guest-js/init.ts:12-18`](https://github.com/tauri-apps/plugins-workspace/blob/v2/plugins/notification/guest-js/init.ts)):
```ts
if (window.Notification.permission !== 'default' || __TEMPLATE_windows__) {
return await Promise.resolve(window.Notification.permission === 'granted')
}
return await invoke('plugin:notification|is_permission_granted')
```
`__TEMPLATE_windows__` is replaced with the literal `true` on Windows,
so the `||` short-circuits and the shim compares its own
freshly-initialised `'default'` against `'granted'` -- `false` -- and
stamps **`denied`**. The line that would ask the backend is unreachable,
and the backend would have said yes: `permission_state()` returns
`PermissionState::Granted` unconditionally on desktop.
So on every launch of the Windows app, `window.Notification.permission`
is `denied` and nothing in the OS is denying anything.
## Why the toggle is only half of it
`getDesktopNotificationPermissionState()` trusts that value, so
`refreshPermission()` reports `denied` at mount, and this effect in
`hooks.ts` runs before the user touches anything:
```ts
React.useEffect(() => {
if (settings.desktopEnabled && (permission === "denied" || permission === "unsupported")) {
setSettings((current) => ({ ...current, desktopEnabled: false }));
}
}, [permission, settings.desktopEnabled]);
```
It writes `desktopEnabled: false` and persists it. Measured on a real
install: with alerts successfully enabled and `desktopEnabled` persisted
as `true`, a clean relaunch comes back with it persisted as `false`.
That means fixing only the enable path leaves a Windows user re-enabling
alerts after every restart.
## What this changes
One place: `getDesktopNotificationPermissionState()` repairs the bogus
value instead of reporting it.
```ts
if (
window.Notification.permission === "denied" &&
isTauri() &&
isWindowsPlatform()
) {
try {
return await requestDesktopNotificationAccess();
} catch {
return window.Notification.permission;
}
}
```
`requestPermission()` is the only call that reaches the backend, and on
Windows it raises no prompt, returns `Granted`, and rewrites the shim's
cached value -- so this is self-limiting: the next read short-circuits
as `granted` and never requests again. There is a test for exactly that.
Repairing at the read rather than at the toggle fixes every consumer at
once, including `sendDesktopNotification()`, which gates delivery on
`=== "granted"` and would otherwise drop notifications at boot.
- `denied` stays terminal on macOS, on Linux, and on ordinary Windows
web pages.
- A denial that survives the request is still reported as `denied`.
- A rejected request falls back to the current value instead of
propagating; callers do not handle rejections today.
- Adds `isWindowsPlatform()` to `shared/lib/platform.ts`, alongside the
existing `isMacPlatform()` / `isLinuxPlatform()`.
- No new dependencies. No changes to `hooks.ts` or to notification
delivery.
## Verification on a real Windows 11 install
Buzz Desktop 0.5.9 release build, Windows 11 Home 10.0.26200, WebView2
151.0.4129.72, attached over CDP. Clean boot, nothing injected:
```
window.Notification.permission -> "denied"
localStorage[...].desktopEnabled -> false (written by the effect above)
await window.Notification.requestPermission() -> "granted"
window.Notification.permission -> "granted"
new window.Notification("Buzz", { body: ... })
ToastNotificationManager::History
.GetHistory("xyz.block.buzz.app") -> 3 -> 4 (real toast delivered)
CreateToastNotifier(...).Setting -> Enabled
```
The OS was permissive throughout: no `ToastEnabled` override, no
notification policy keys under HKCU or HKLM, and the app present under
`HKCU\...\Notifications\Settings\xyz.block.buzz.app`. Full detail in
[this
comment](https://github.com/block/buzz/pull/2483#issuecomment-5255972424).
To be precise about scope: this confirms the mechanism the patch relies
on, measured on a stock release build. The patched build itself is
covered by the unit tests below, not by a packaged Windows run.
## Tests
`pnpm test` -- full desktop suite. New cases in `lib/desktop.test.mjs`:
- Windows Tauri repairs the shim's false denied state on read
- the repaired state is cached, so later reads do not request again
- a denial that survives the request is reported as denied
- denied stays terminal outside the Windows Tauri app (Windows web,
Linux Tauri, Linux web)
- granted is returned untouched and never triggers a request
Plus `shared/lib/platform.test.mjs` for `isWindowsPlatform()` across
`Win32` / `Win64` / `Windows` and `MacIntel` / `Darwin` / `Linux
x86_64`.
## Relationship to #2483
#2483 fixes the same root cause at the toggle: it retries the request
inside `setDesktopEnabled`. That makes the toggle work, which is what
#2445 reports, and its `ensureDesktopNotificationPermission` helper is a
nicer shape than an inline condition.
The difference is where the repair happens. Because #2483 leaves the
mount-time read as `denied`, the effect quoted above still turns the
setting off on every launch, so the fix does not survive a restart.
Repairing at the read covers the toggle path too, since
`setDesktopEnabled` calls `refreshPermission()` first and finds
`granted`.
The two overlap: both add `isWindowsPlatform()` to `platform.ts`, so
whichever lands second needs a trivial rebase. If maintainers prefer
#2483's shape, the equivalent of this PR is to call its helper from
`refreshPermission` as well as from `setDesktopEnabled` -- I am glad to
close this and send that instead. I did not want to push changes into
someone else's open PR uninvited.
## Once this lands
#2445 can close. I am running a per-machine launcher workaround for a
small Windows team until then, which this makes unnecessary.
Signed-off-by: VSCteam <144167621+Joxyko@users.noreply.github.com>
* test(desktop): move CSP guards from Rust to the desktop JS suite (#8172)
## Summary
Moves the packaged-app CSP guards from `desktop/src-tauri/tests/csp.rs`
to `desktop/src/app/contentSecurityPolicy.test.mjs`. No production code
changes beyond one added `export`.
`csp.rs` never touched Rust app code. All seven tests parse
`tauri.conf.json` and compare CSP strings. The MediaPipe check also
`include_str!`'d
`desktop/src/features/profile/lib/animatedAvatarCapture.ts` and pulled
the `MEDIAPIPE_WASM_BASE` literal out by splitting the text. That made a
Tauri test depend on a frontend file. With path-filtered CI (#8156), a
change to only that `.ts` file would skip the check.
The JS version imports `MEDIAPIPE_WASM_BASE` directly (it's now
exported) and reads `src-tauri/tauri.conf.json` from disk. The
`desktop/**` CI filter covers both files, so the check runs in Desktop
JS whenever either one changes, and the filter needs no cross-boundary
special case.
The seven tests and their assertions carry over one-for-one, along with
their rationale comments.
**What got simpler:** we delete a 204-line Rust integration test, the
`include_str!` of a frontend file, and the hand-rolled string-literal
scraper, and the CI path filter doesn't need to know about this file.
### Related issue
Addresses the CSP coupling raised in review of #8156. Related: #4614
(introduced the guards).
### Testing
- New suite on Linux: 7/7 pass.
- I falsified each test by mutating the real policy or code, one
mutation at a time. Each mutation fails exactly the matching test, and
the suite passes again once restored:
- moved `MEDIAPIPE_WASM_BASE` outside `@mediapipe/`
- dropped `'wasm-unsafe-eval'`
- dropped the MediaPipe scope from `script-src`
- added a bare `https://cdn.jsdelivr.net/` origin
- added `'unsafe-inline'`
- removed `img-src`
- dropped `ws:` from `connect-src`
- made the pinned-source predicate always pass
- Blox `just ci` at tree `5664c6ce` (same tree as head `f798f94b`):
- Passed: fmt, clippy, desktop/Tauri/web checks,
security-review/file-size checks, `desktop-test` (6,819 + 139 jsdom),
`desktop-build`, `desktop-tauri-check`, `desktop-tauri-test`,
`web-build`.
- `test-unit`: 94/95 suites pass. The two failing `buzz-acp`
`git_bootstrap` tests fail because the workstation's Git 2.43 predates
the credential `authtype` protocol. They pass 4/4 with Git 2.51, and
this PR touches no `crates/`.
- Not run: `mobile-check`/`mobile-test`, because the workstation can't
reach pub.dev. No `mobile/` changes.
- Hosted CI green:
https://github.com/block/buzz/actions/runs/37801901659. This PR selects
the Tauri lanes because it deletes `src-tauri/tests/csp.rs`. Later edits
that only touch the constant select Desktop JS only.
---------
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Co-authored-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
* chore(release): release Buzz Desktop version 0.5.28
Co-authored-by: Release Automation <release-automation@users.noreply.github.com>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
---------
Signed-off-by: tornquist <tornquist@squareup.com>
Signed-off-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Signed-off-by: Ian Oberst <ioberst@block.xyz>
Signed-off-by: am <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <pfleger.will@gmail.com>
Signed-off-by: Paul <4a1bfa0013bc6d14a8d600d8bf6392efefbd2a26ac3c96c9b2a106b0d12297ca@buzz.block.builderlab.xyz>
Signed-off-by: Tom Brow <tomb@block.xyz>
Signed-off-by: VSCteam <144167621+Joxyko@users.noreply.github.com>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Co-authored-by: Luke Tornquist <tornquist@squareup.com>
Co-authored-by: Claude Opus 5 <noreply@anthropic.com>
Co-authored-by: Elrond <28d6302a099e5225b02c4155ac4236e4912603df2ab08dbfc2f4fef08ce598c8@buzz.block.builderlab.xyz>
Co-authored-by: Ian Oberst <ioberst@squareup.com>
Co-authored-by: Ian Oberst <ioberst@block.xyz>
Co-authored-by: Kalvin C <kalvinnchau@users.noreply.github.com>
Co-authored-by: am <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@buzz.block.builderlab.xyz>
Co-authored-by: Will Pfleger <pfleger.will@gmail.com>
Co-authored-by: Paul <4a1bfa0013bc6d14a8d600d8bf6392efefbd2a26ac3c96c9b2a106b0d12297ca@buzz.block.builderlab.xyz>
Co-authored-by: Tom Brow <tomb@block.xyz>
Co-authored-by: VSCteam <144167621+Joxyko@users.noreply.github.com>
Co-authored-by: Will Pfleger <wpfleger@block.xyz>
Co-authored-by: Release Automation <release-automation@users.noreply.github.com>


Summary
Moves the producer side of the two event follow-up triggers into application code. The triggers stay in place, so both producers run until a later change drops the triggers after this ships to every pod.
Builds on #8130 (
AdmittedTx). Refs BUZZ-176.Push match enqueue
New
store::event_follow_up::enqueue_push_matchreplaces theevents_enqueue_push_matchtrigger (schema/functions/enqueue_push_match_job.sql, migration 0023) and matches it exactly:PUSH_MATCH_KINDS.buzz_push_gate:<community>advisory lock as its own statement, so under READ COMMITTED the lease check gets a snapshot taken after the lock is granted. Lease activations still take it EXCLUSIVE inpush.rs.active AND endpoint_enabled AND expires_at > now), thenINSERT push_match_queue ... ON CONFLICT DO NOTHING.It runs right after the INSERT, only when the insert affected a row. The consumer side (claims,
lease_until, attempts, reaper) is already app-owned and is unchanged.Channel TTL refresh
AdmittedTxnow records every channel that received an event (except kind 9007 and channel-less events).AdmittedTx::commit()refreshes theirttl_deadlineas the last statement before COMMIT, which keeps the commit-time behavior of the deferredevents_refresh_channel_ttltrigger (migration 0024):buzz_channel_ttl:<community>:<channel>lock.UPDATEwith the samearchived_at/deleted_atfilters as its own statement after the lock, so its snapshot follows the lock grant. Itsttl_seconds IS NOT NULLqual filters a permanent channel before any tuple lock, so a permanent channel's row is never locked. An ephemeral channel's row lock is held through the remaining refreshes and the COMMIT round trip (the trigger held it only inside COMMIT).channel::channel_ttl_lock_key,push::push_gate_lock_key), shared by the SHARED and EXCLUSIVE sides. The shared push-gate wait is observed throughobserve_advisory_lock(LockType::PushGate, …).buzz_db_channel_ttl_refresh_failures_total{reason}, wherereasonislock_timeoutorerror. The event still commits, matching the trigger'sEXCEPTION WHEN OTHERS. A cancelled statement (57014) still rejects the transaction, because plpgsql never caught that either.lock_timeoutis counted, and then the trigger retries it inside COMMIT and may succeed. So during the dual window the failure counter can over-report and the worst-case wait doubles. Both go away when the retirement PR drops the triggers, after which the counter is exact.Call sites
Every production
INSERT INTO eventscallsevent_follow_up::after_admitted_insert:insert_event_oninsert_event_with_thread_metadata_txLockedMemberSnapshot::replace_member_eventreplace_addressable_eventpublish_nip43_membership_lockedaccept_lease_event(kind 30350, a no-op today, kept so the policy has no exceptions)replace_parameterized_event_in_transaction_implinserts inside theparameterized_replacesavepoint. It enqueues the push job inside the savepoint, so a rollback to that savepoint also drops the job, and records the TTL channel only after the savepoint is released.The two rolled-back verification probes (
verify_floor_guard_behavior,verify_channel_roster_fence_behavior) are named exceptions, because they never commit.Source policy
tests/observability_source.rsaddsevery_production_event_insert_runs_the_follow_up_hook. It scans everycrates/*/srcand fails on any function that inserts intoeventswithout the hook. Matching is normalized (letter case, whitespace,\continuations,\n/\t/\rescapes, optionalpublic.). The file is masked once first: comments (//, nested/* */) and string, raw-string (includingbr"/cr"), and char literals become spaces.#[cfg(test)]markers,fnsignatures and the hook are all found in that masked view, so a marker in a comment (even a multiline block comment) strips nothing, anfnline inside a multiline string doesn't split a function, and a commented-out or quoted hook doesn't count. SQL is still matched in the original text. A table test pins the masker's output for each literal form. A fixture test pins what the scan rejects (no hook, push without TTL, a hook in a line comment, block comment, or string, lowercase or line-broken or escaped SQL, writers after test-only items or under comment mentions) and what it ignores (writers in#[cfg(test)] mod). A floor of seven hooked writers catches a scan that silently stops seeing writers.Tests
src/store/event_follow_up_postgres_tests.rsis the contract suite from the BUZZ-176 discovery work, ported to theAdmittedTxAPI. It is a crate-internal#[cfg(test)]module because it runsSET LOCALtimeouts and in-transaction reads through the crate-privateAdmittedTx::conn(). It runs on both the desired and migration schemas, in two arms:The trigger-only baseline is the base branch, where the same suite passed before this change. The suite also pins the two branches that differ from "swallow everything": a
lock_timeoutfailure incrementsbuzz_db_channel_ttl_refresh_failures_total{reason="lock_timeout"}exactly once, and a statement cancel (57014) during the refresh rejects the event with no row, job, or deadline change.What got simpler
Nothing yet. This adds a parallel producer during the migration window. It is what lets the follow-up PR delete two plpgsql functions, two triggers, and the "keep in sync with migrations/00xx" duplication between
schema/functions/andpush.rs.Verification
Rebased onto
main@e9269cbdf. The head is now184cbb2e8. All runs used a Linux cloud workstation with the pinned toolchain (rustc/clippy 1.95.0, hermit), and the tree was clean before and after each run.Production source changed since
1eb11bde. The rebase took in #8178. That PR removedbackfill_push_match_jobsand both of its call sites frompush.rs, and this PR'sevent_follow_up.rsdocs were reworded to match (51664d60c). So the evidence pinned to1eb11bdeandc5a06a82below is history. It does not describe today's runtime tree byte for byte.184cbb2e8changes only test code (the char-literal masker incrates/buzz-db/tests/observability_source.rs).Evidence at the current head
184cbb2e8:cargo test --locked -p buzz-db --test observability_sourcepassed 17/17 on macOS, run by the reviewer.e9269cbdf…184cbb2e8and reported risk NONE.Descendant evidence: #8210 at
6be64d87ais this head plus migration 0058, which drops the retired triggers. On the cloud workstation it passed fmt, clippy, policy, lib, buzz-db PG (486) and buzz-relay PG (378).cargo fmt --check,cargo clippy -p buzz-db --all-targets -D warningsfbc9a598cargo clippy(workspace)1eb11bde--test observability_source), fmt, buzz-db clippyc5a06a82cargo test --locked -p buzz-db(non-PG)c5a06a82--test observability_source)fbc9a598cargo test --locked -p buzz-db(non-PG)fbc9a598store::event_follow_up_postgres_tests, desired/migration × dual/app-only)1eb11bde1eb11bde1eb11bdefbc9a598Falsifications (each mutation made the named test fail, then was reverted):
relay_membershook → policy namespublish_nip43_membership_locked57014→ all four arms fail#[cfg(test)]match, or no escape handling → fixture test fails#[cfg(test)]constructor that skips admission, added insideimpl AdmittedTx(indented or as a column-0mod) →admitted_tx_is_constructed_only_by_admitting_constructorsfails; putting the strip back into the constructor scan → its fixture test fails7c0baa41:accept_lease_event's hook commented out and the real call made through an alias → policy namesaccept_lease_event(the same mutation passes under thefbc9a598policy); hook matching on unmasked text → the comment/string fixtures fail9199992c/d405b2f6: no nested block-comment depth, no string-escape skip, nobr"/cr"raw-literal prefix, or no raw-string branch at all in the masker → the follow-up fixture test failsc5a06a82: finding#[cfg(test)]in the unmasked text →writer_after_block_commented_cfg_testis no longer reported; findingfnsignatures in the unmasked text →writer_after_raw_string_exampleis no longer reported; nocrraw prefix → the masker table test fails oncr"side_effects.rs(after test-only items, under a doc-comment mention, with an escaped newline) → policy names eachLive relay E2E: an independent reviewer ran this at
1eb11bdeagainst a real relay and CLI, with PostgreSQL 17 and Redis 7, the follow-up triggers absent, and no partition clones.push_match_queuerow with the same event id.Limits: the push lease was a SQL fixture, and push consumers were disabled. Kind 30023 is global, so channel-scoped TTL on the parameterized path is covered only by the PG contracts. No live relay rerun was done at
fbc9a598, because that delta is test-only.Latency (measured at pre-rebase
f8380927, same production delta; debug build on loopback, 1,000 samples per cell, EVENT→OK): head app-only p50/p99 3.80/4.58 ms (permanent) and 3.87/4.64 ms (TTL), against base trigger-only 3.49–3.53/4.00–4.03 ms and 3.56–3.62/4.30–4.46 ms. About +0.3 ms p50, from the extra client round trips (lock, UPDATE, savepoints, push lock/insert) that the triggers ran server-side. One debug loopback run, not a production p99.Not measured: contention from many writers on one hot TTL channel, where each writer now waits on the channel row lock for about two more client round trips (RELEASE SAVEPOINT and COMMIT) than with the trigger. In review, a burst of 8 concurrent posts to one TTL channel committed with no deadlock or lock timeout. Watch send p99 and
pg_lockswaits onchannelsduring rollout.Known pre-existing, not touched here:
api::mesh_demo::tests::demo_join_forwarded_arm_round_trips_echois flaky when Redis is present. It returns a 504 in 4 of 5 runs at base745501962and 2 of 5 atfbc9a598, always at the same assertion. No CI lane selects it.