Repository navigation
Fix bot dashboard and augurScan UI review findings - #1114
Merged
Merged
Conversation


github-merge-queue
Bot
removed this pull request from the merge queue due to failed status checks
Oct 3, 2026
github-merge-queue
Bot
removed this pull request from the merge queue due to failed status checks
Oct 3, 2026
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
1 participant

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
What
A source review of the three bot operator dashboards (
bots/chaos,bots/liquidator,bots/open-oracle-arbitrager), their shared console kit (bots/shared/src/dashboard) and the augurScan explorer found one high-severity theming bug, five high-severity augurScan bugs and a longer list of medium/low ones. This PR fixes them.Why and what changed
Shared bot console (
bots/shared)color-scheme: light dark, and the console pinned only some colours, so--accent-ink,--infoand--border-strongresolved to light values (primary button text at ~1.4:1).color-scheme: darkis now pinned.createFocusedFormSubmitterrenders failures in the error style withrole="alert".[hidden]rule so the attribute always hides in the dashboards.requestJsonreads the response body inside the timeout; abeforeunloadguard protects dirty tracked forms; scroll offsets only subtract the header when it is sticky; universe approval keeps keyboard focus; no duplicate history entries;formatAmountnever renders-0.Chaos
Liquidator
change; a timed-out or rejected switch unlocks the dashboard instead of freezing it.underwritingLimitAttoEth); vault health uses the configured top-up threshold.Open-oracle-arbitrager
augurScan
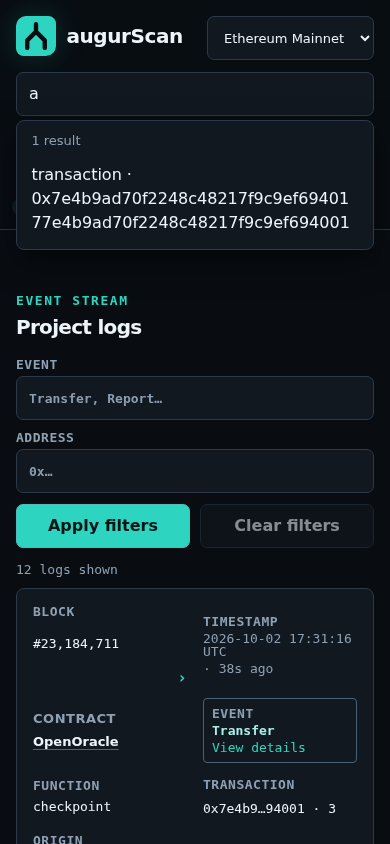
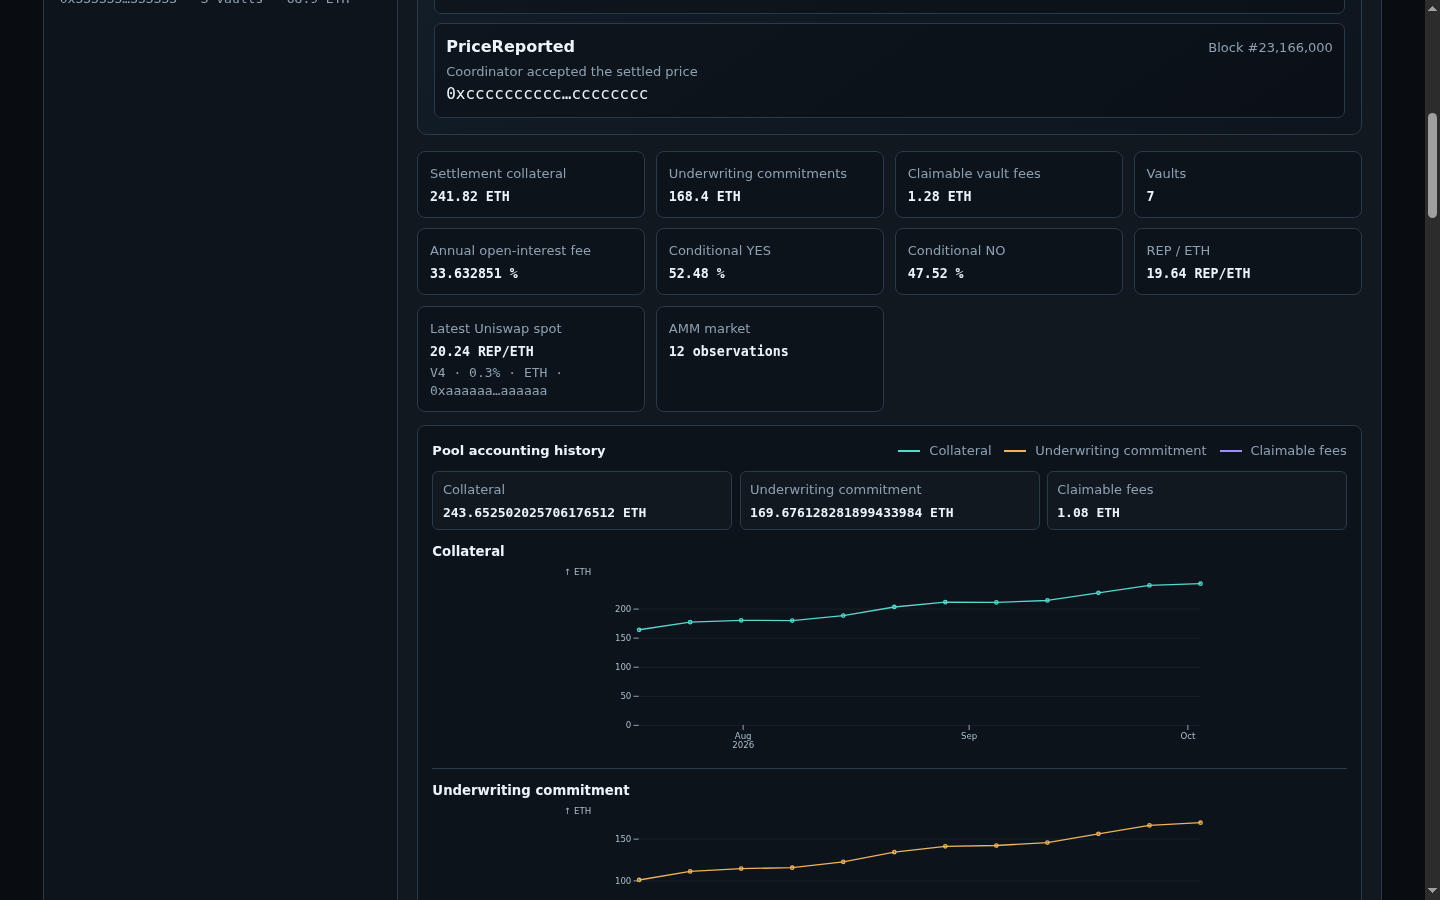
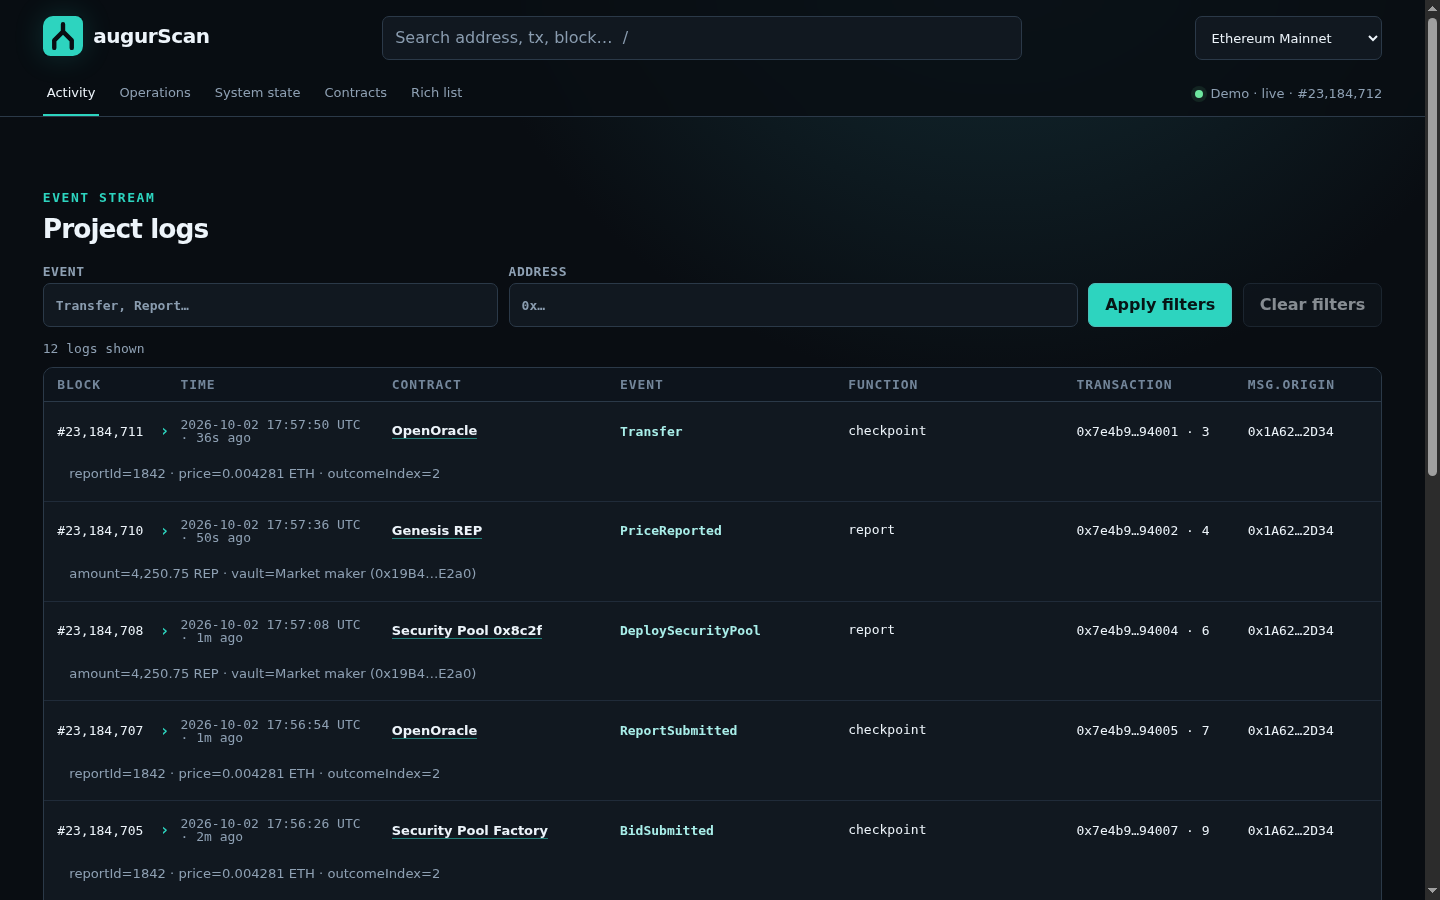
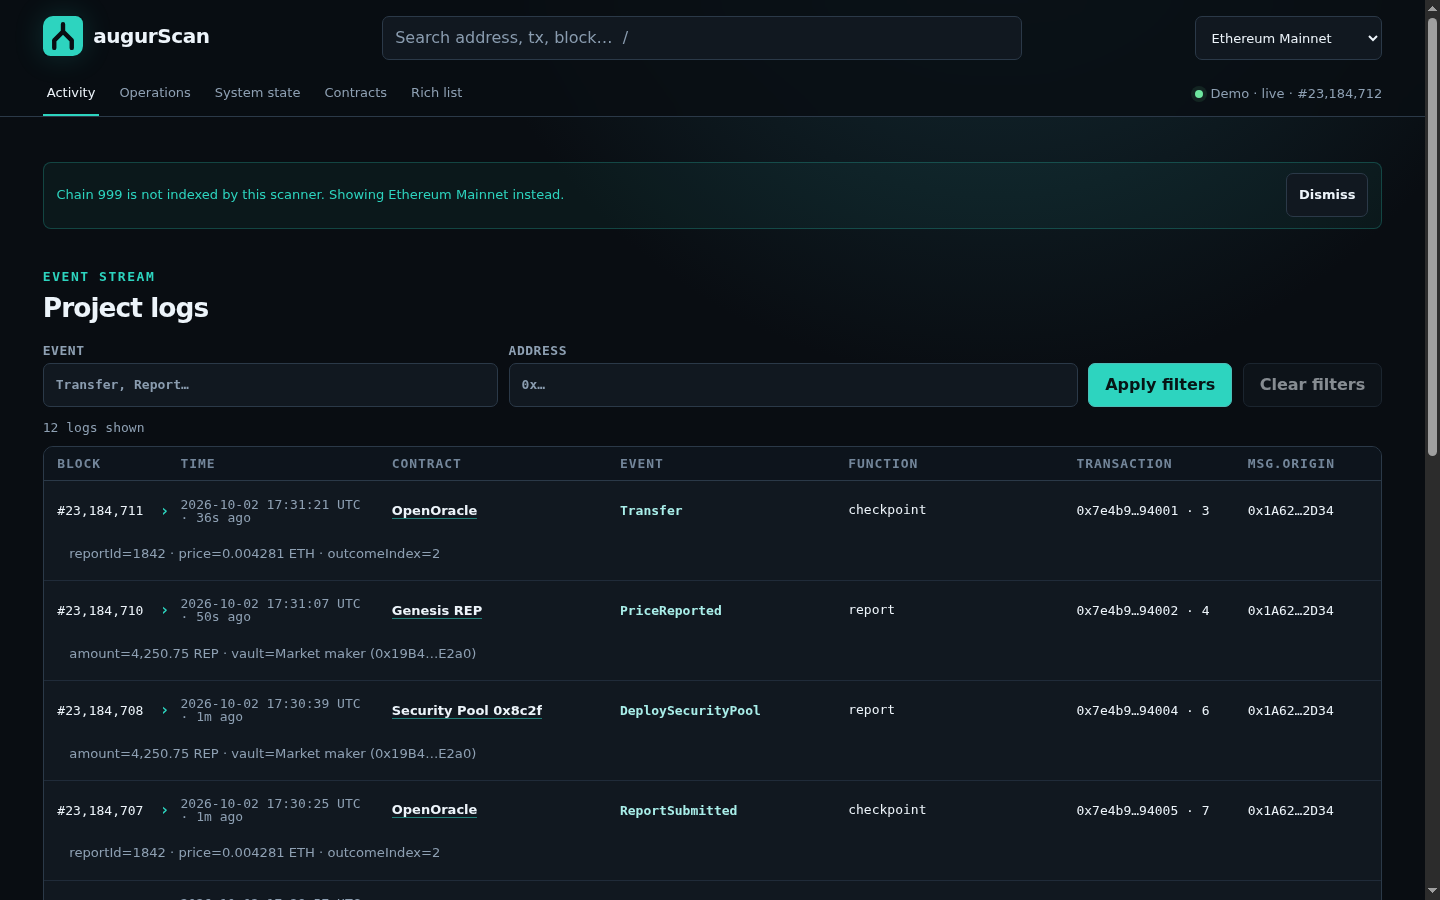
hiddenwas overridden by authordisplayrules (stale "Show more" buttons and error boxes). There is now one global[hidden]rule.<style>is replaced by rules in the stylesheet.chainIdshows a notice.application/octet-streamfallback content type, stricter CSP, minified bundle, dead CSS removed.Dependency audit
bun auditstarted failing for every project on GHSA-vfj7-8cjw-p6xm (braces <= 3.0.3, stack exhaustion on deeply nested brace patterns), which has no patched release.bracesarrives only through@tevm/compiler > solc-typed-ast > findup-sync > micromatch, and its only caller is solc-typed-ast's import resolver, which passes the constant patternnode_modules/; no pattern from this repository, a user or a remote party reaches it. All audits now share one command intooling/repo/projects.tsthat ignores exactly this advisory, with the rationale beside it and a test pinning the accepted list. Remove the entry when a patched release exists.Not covered: the
infrastructure-checksjob in.github/workflows/ci.ymlstill runs a barecd solidity && bun audit(it only runs for infrastructure-only changes). Changing it tobun ./tooling/repo/run-project-tasks.mts audit --project-path solidityneeds a push withworkflowscope.Not in this PR
The arbitrager's forwarded-message allow-lists repeat the validators' message strings rather than sharing constants; if a message is reworded the dashboard falls back to the generic text (nothing leaks). Left for a follow-up.
Cross-bot CSS/request-helper dedupe, splitting augurScan's stylesheet, content-hashed assets, a route registry for augurScan, and unifying loading/empty/error styling.
Validation
bun run tscbun run testinbots/shared(354),bots/chaos(975),bots/liquidator(328),bots/open-oracle-arbitrager(527)bun run test:ci(unit 312, api 66, replay 135) andtests/browseragainst the demo build in headless Chromium (64)bun run format:check,bun run check(includestest:preflight),bun run knip,git diff --checkbun ./tooling/repo/run-project-tasks.mts audit --group core-auditand the bot/augurScan audits: no vulnerabilities, 1 ignoredScreenshots
Headless Chromium against the fixture/demo servers.
Bot dashboards stay dark with a light-mode OS (liquidator,
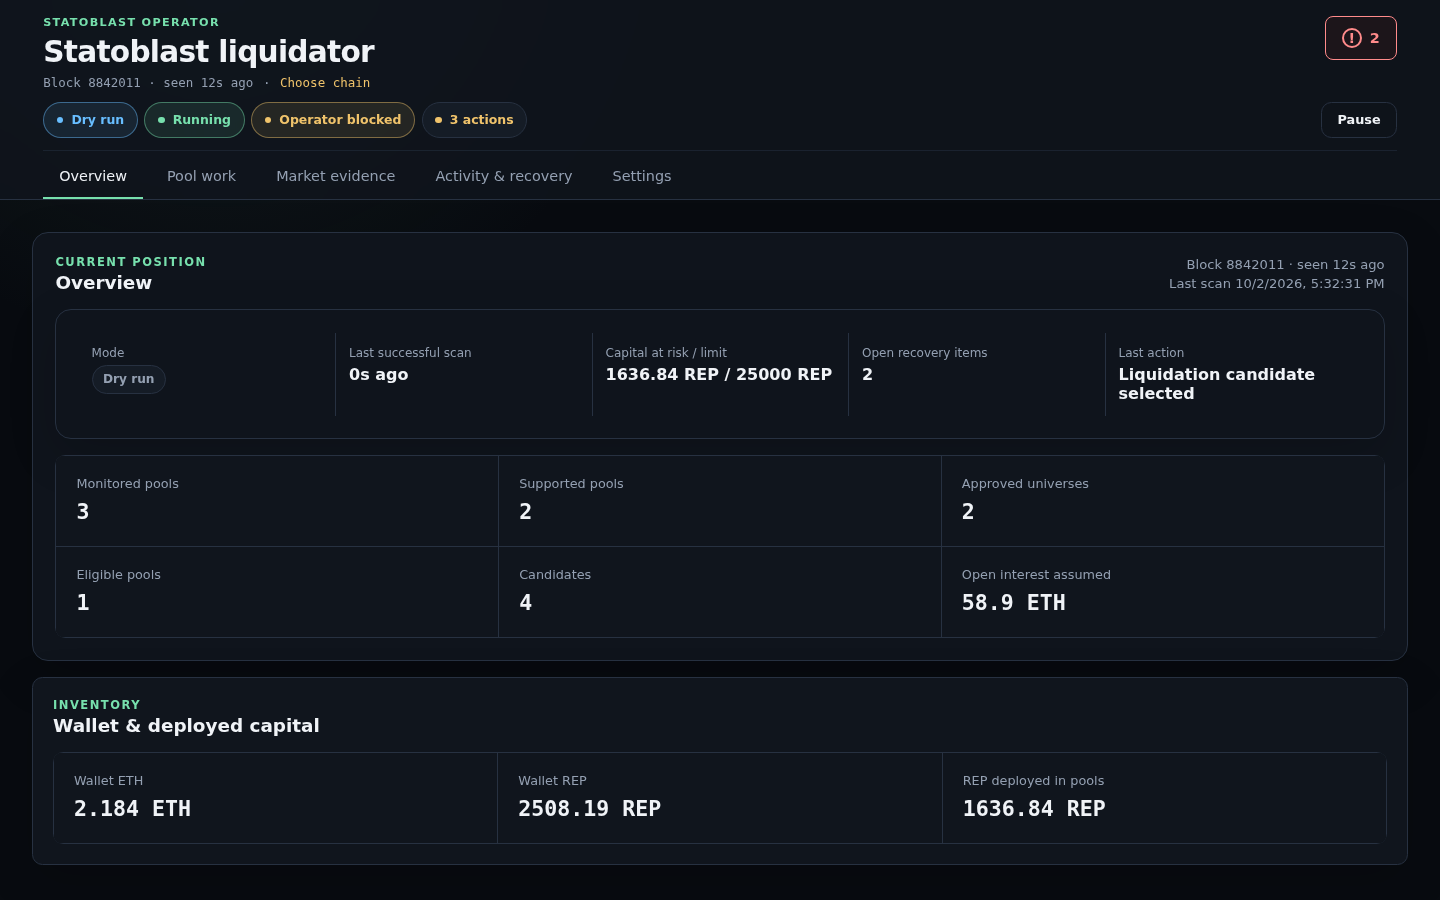
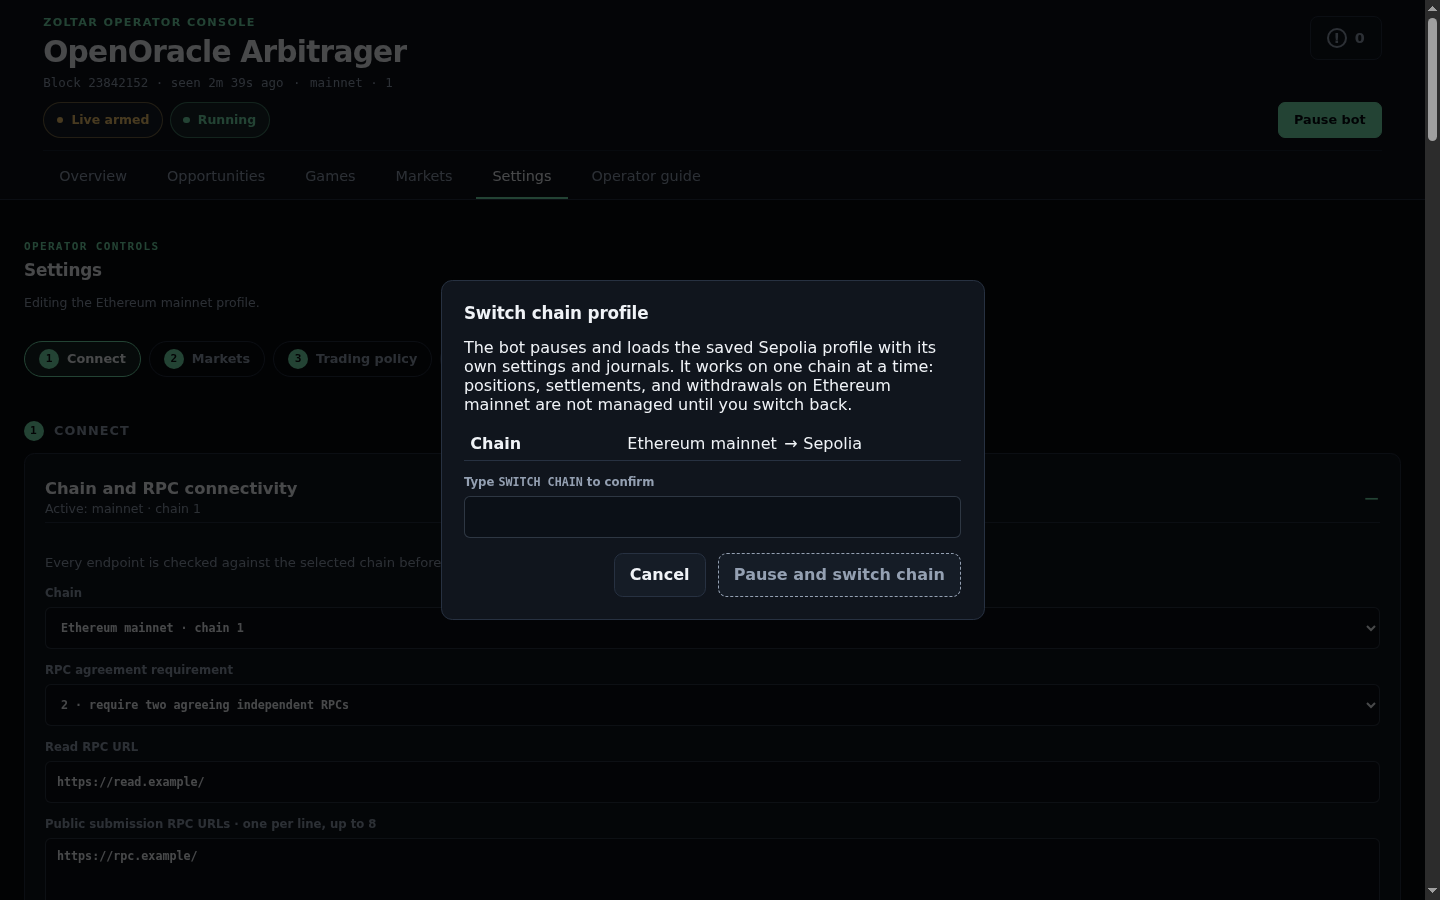
prefers-color-scheme: lightemulated, 1440x900)Chain switch confirmation (liquidator 1440x900 and 390x844; arbitrager live-armed with typed phrase)
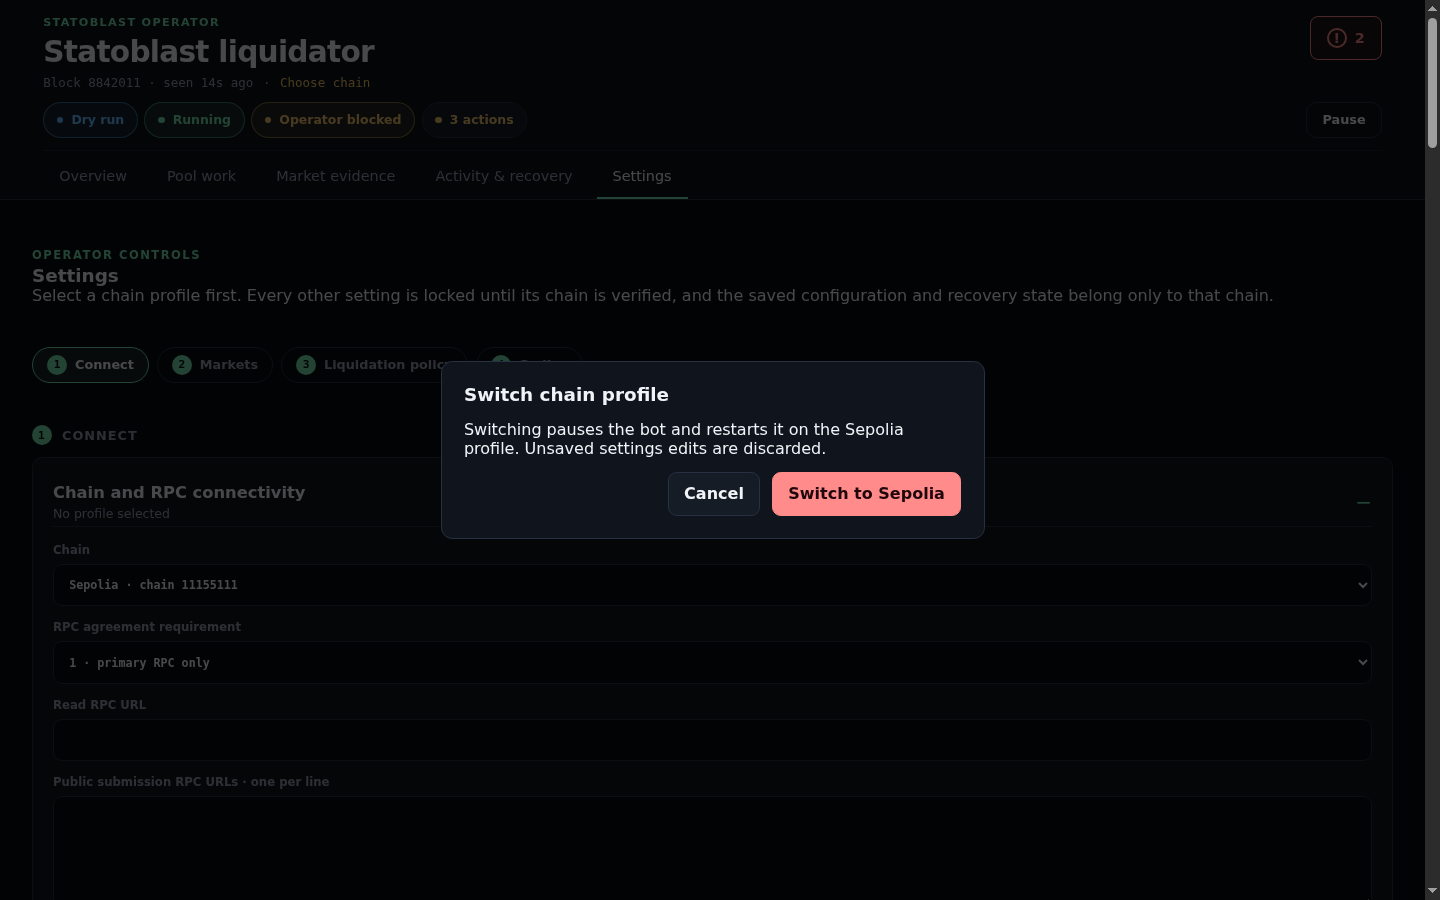
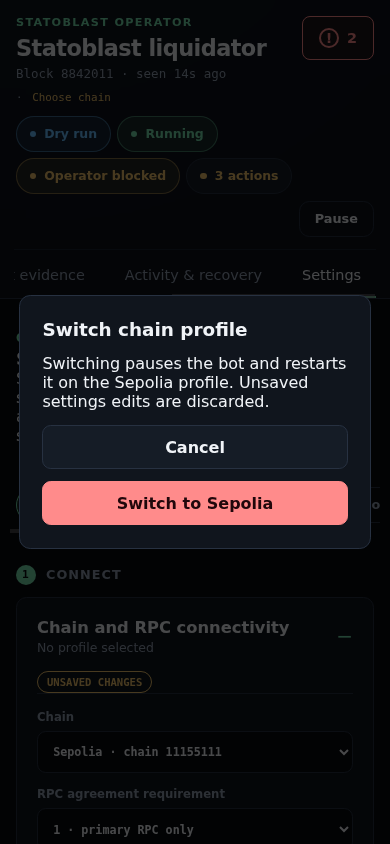
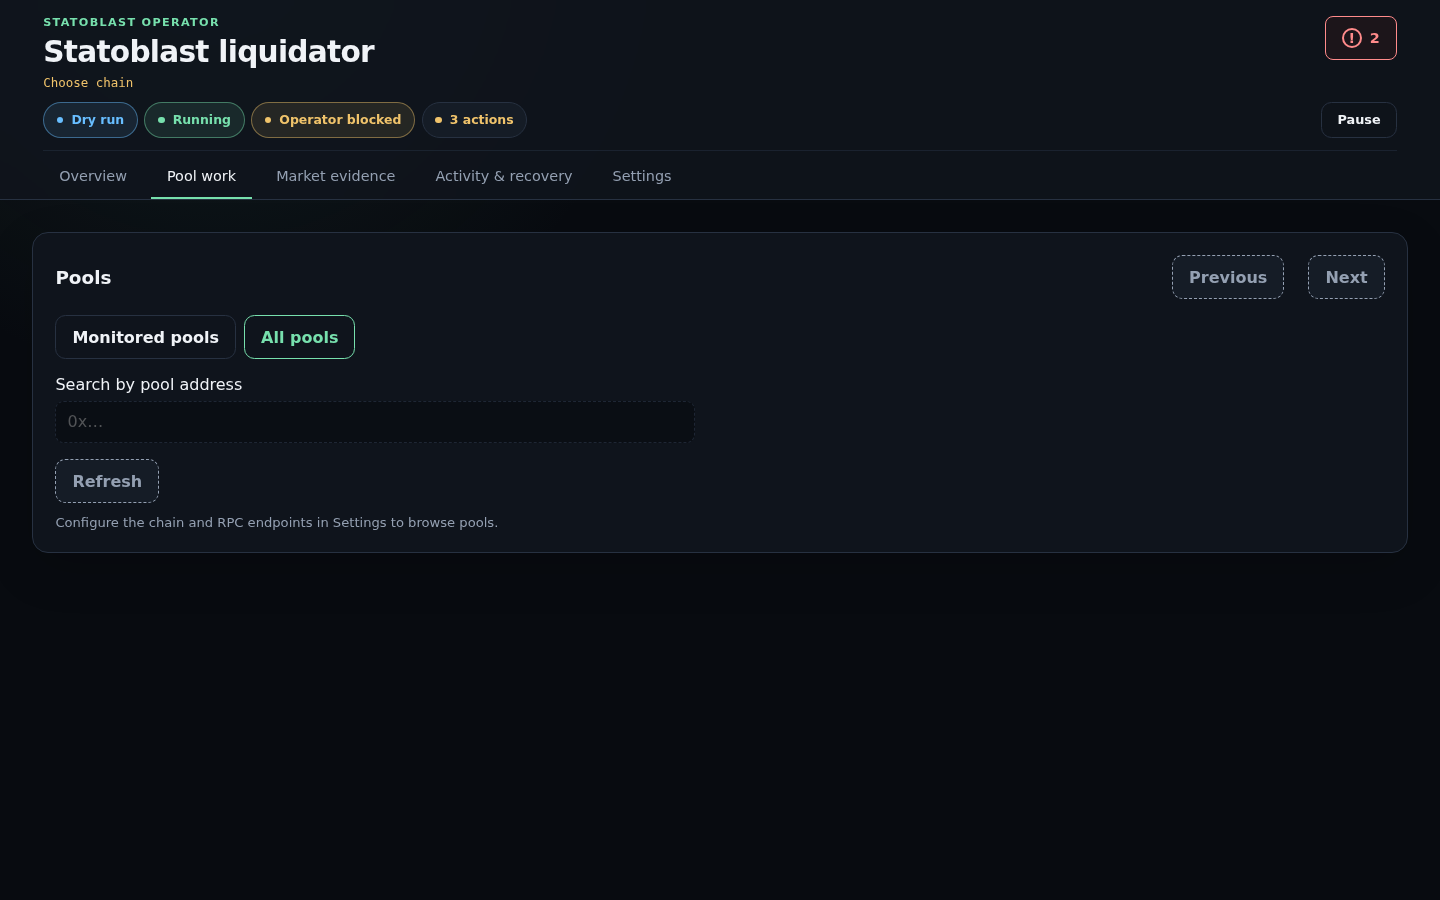
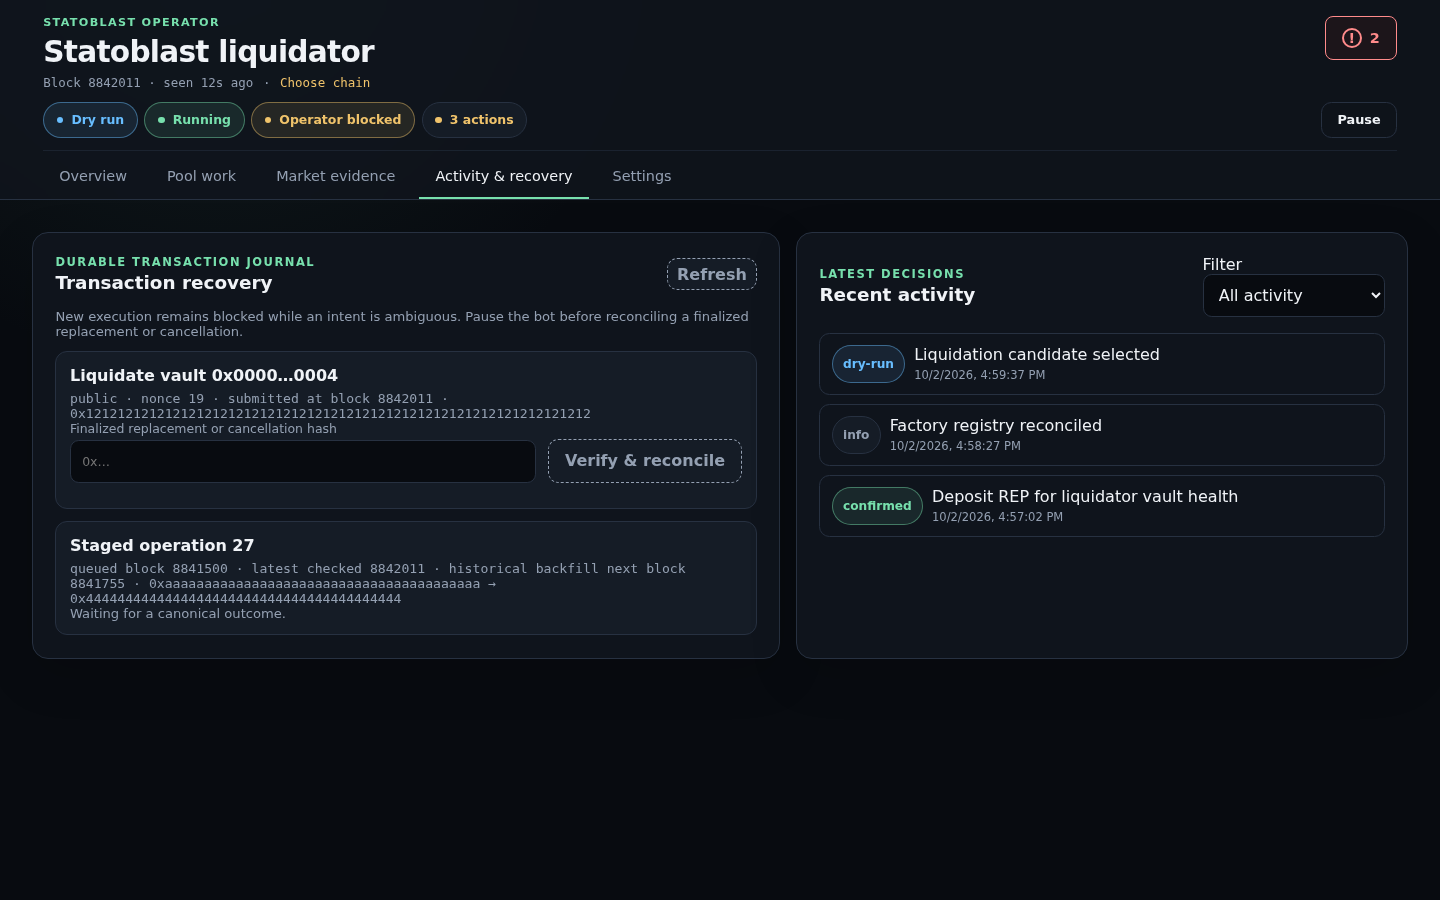
Liquidator pools and transaction recovery (1440x900)
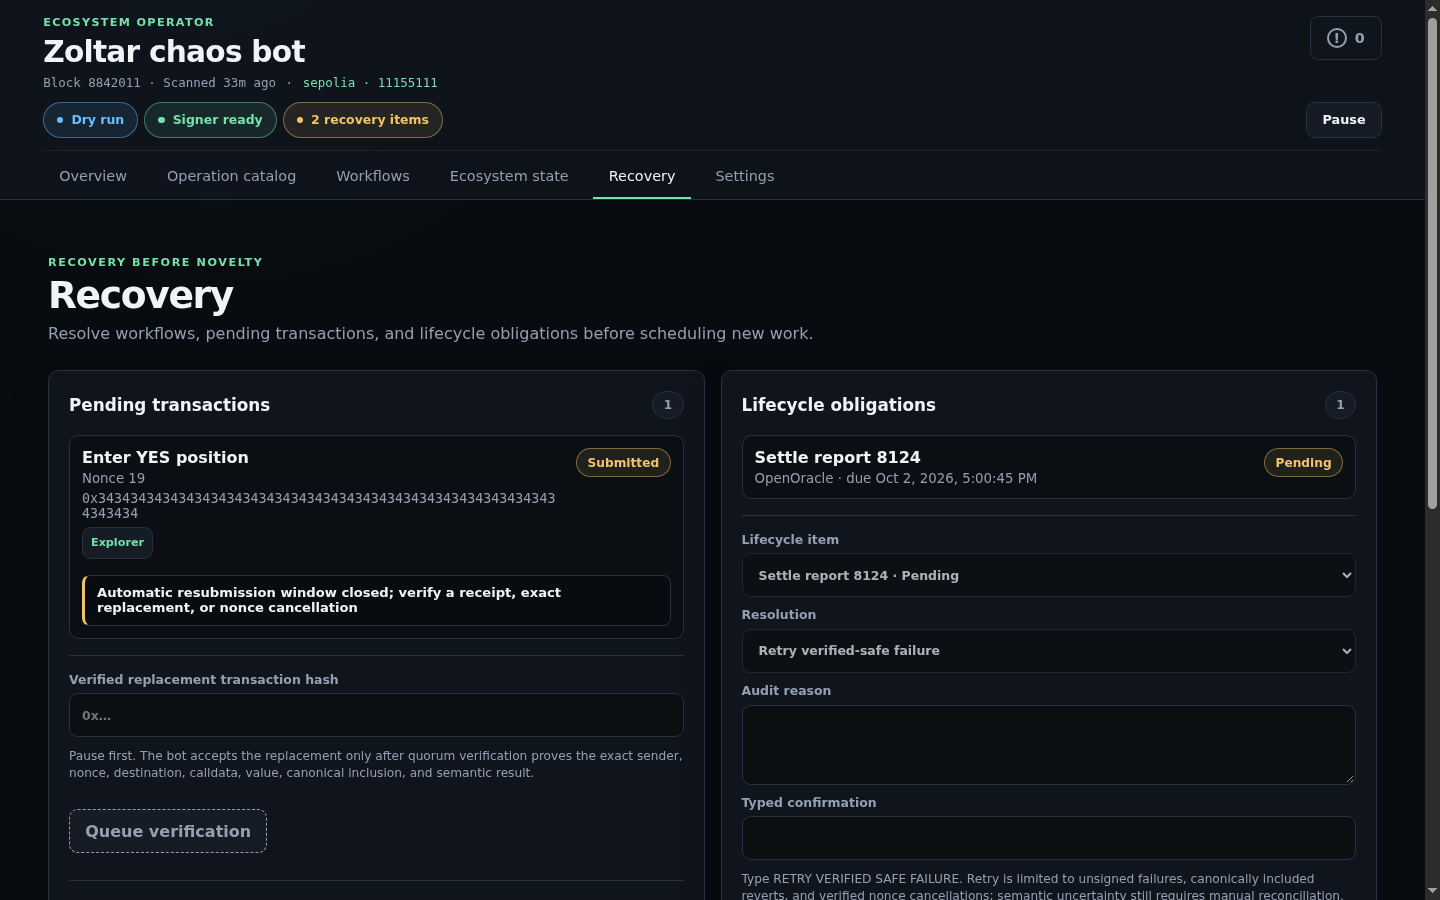
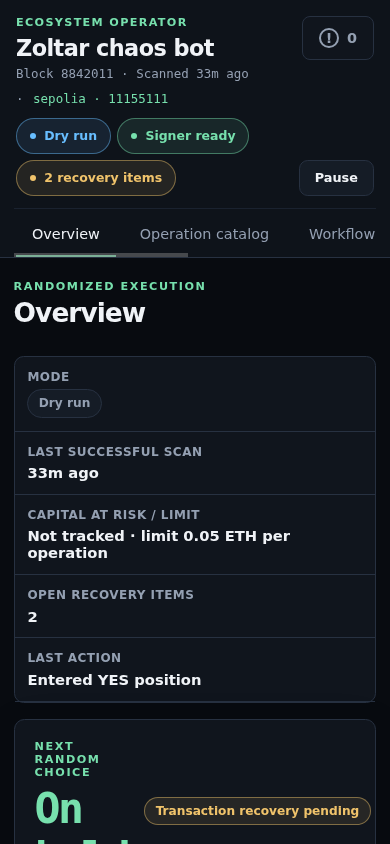
Chaos recovery (1440x900) and overview (390x844)
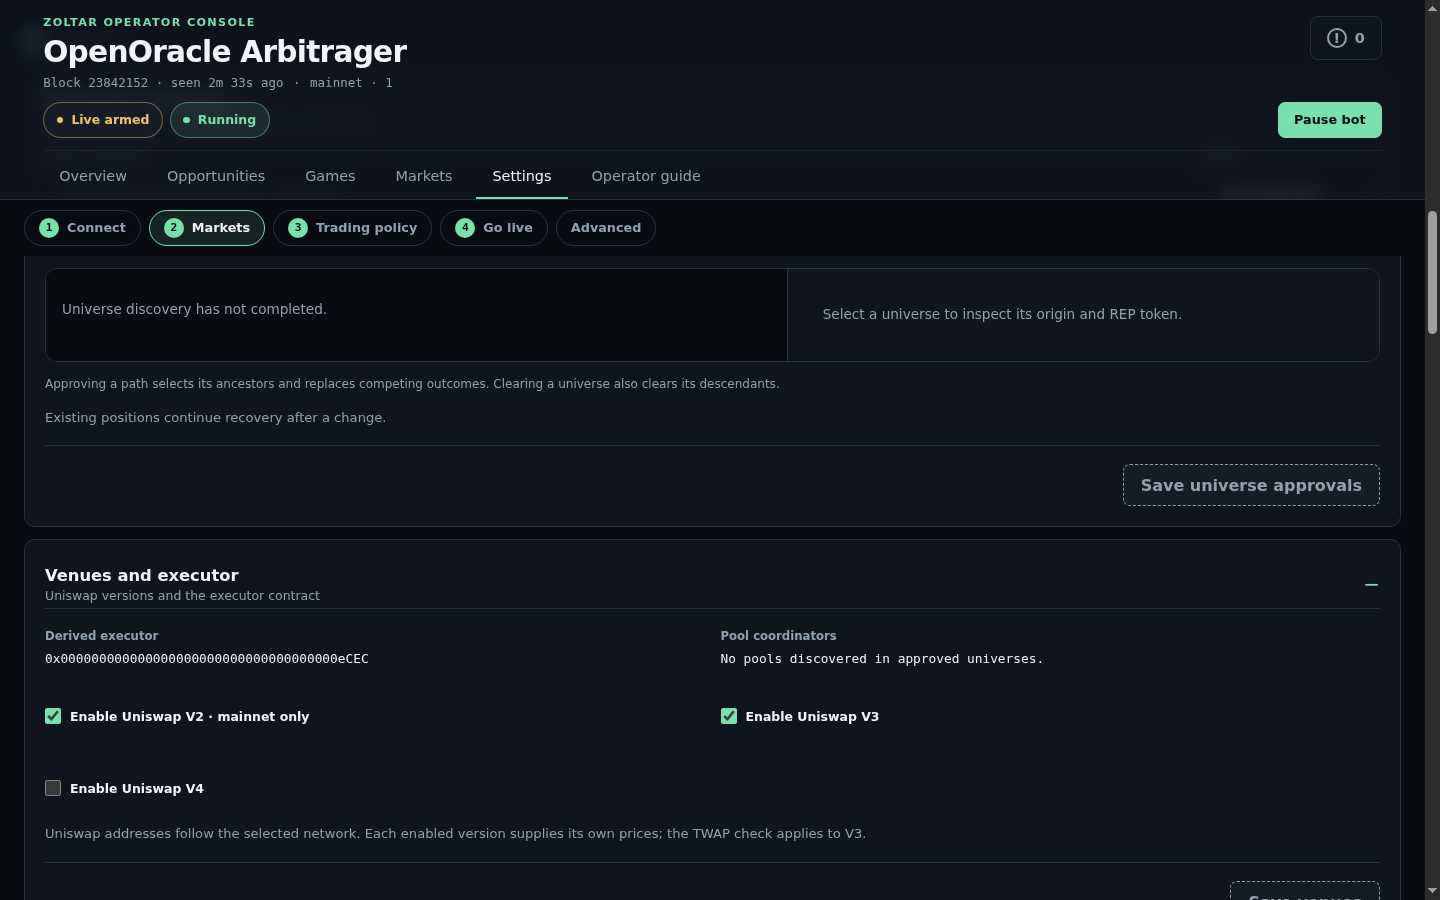
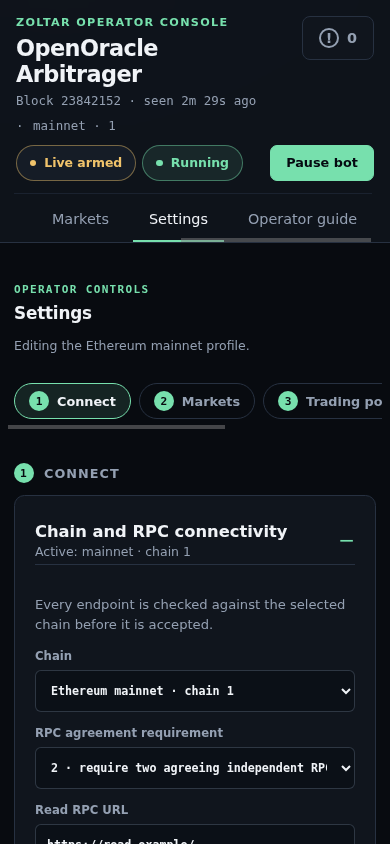
Arbitrager approved universes and settings (1440x900, 390x844)
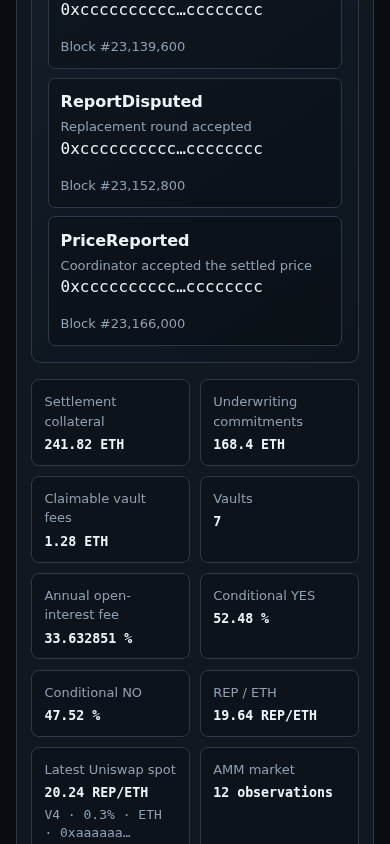
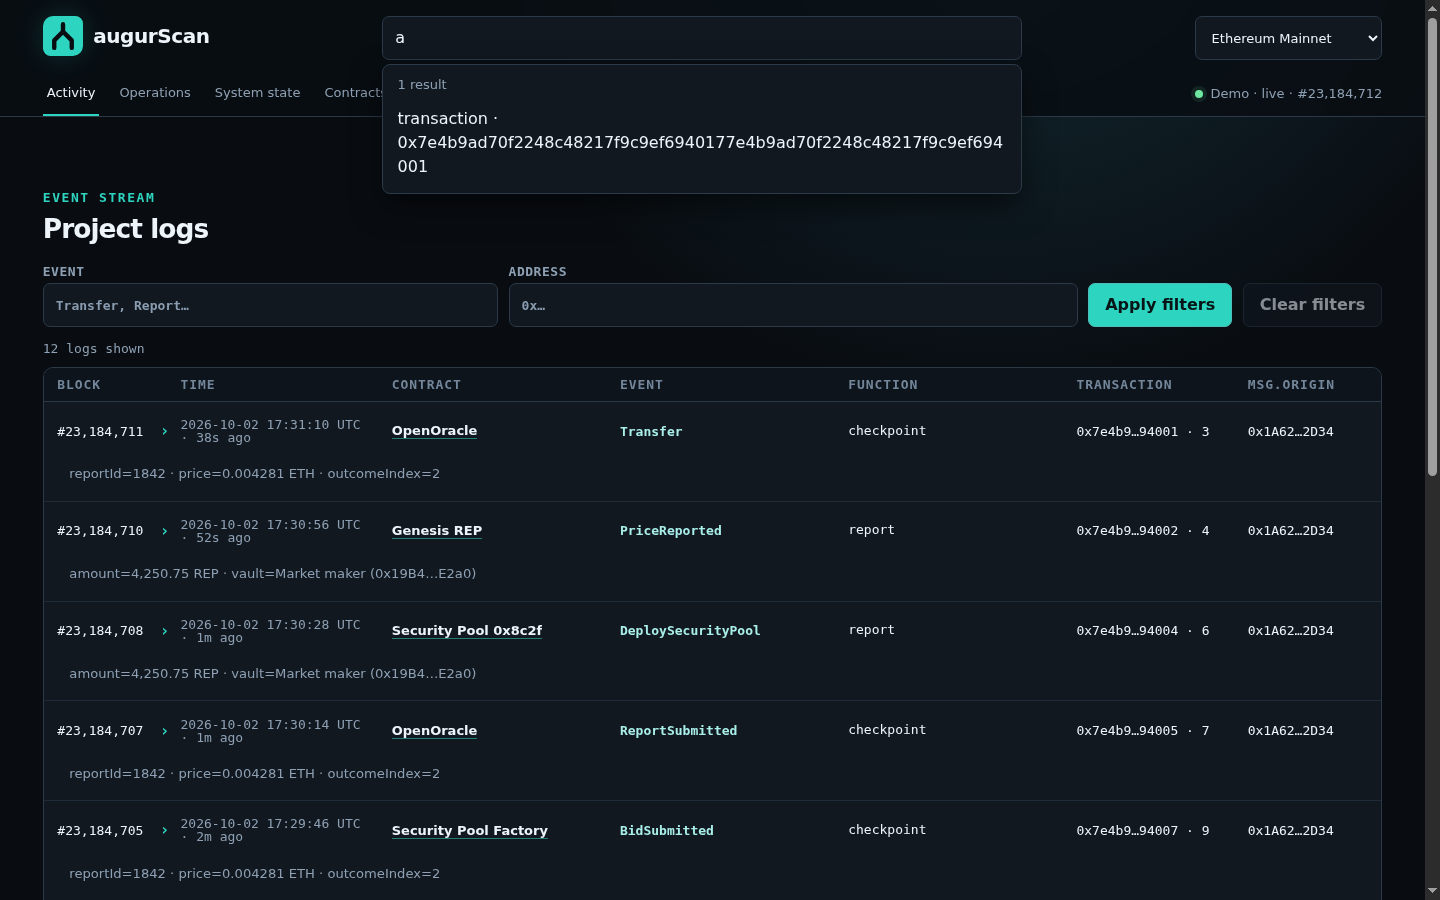
augurScan search overlay (1440x900, 390x844)
augurScan chart legend matches line colours (1440x900)
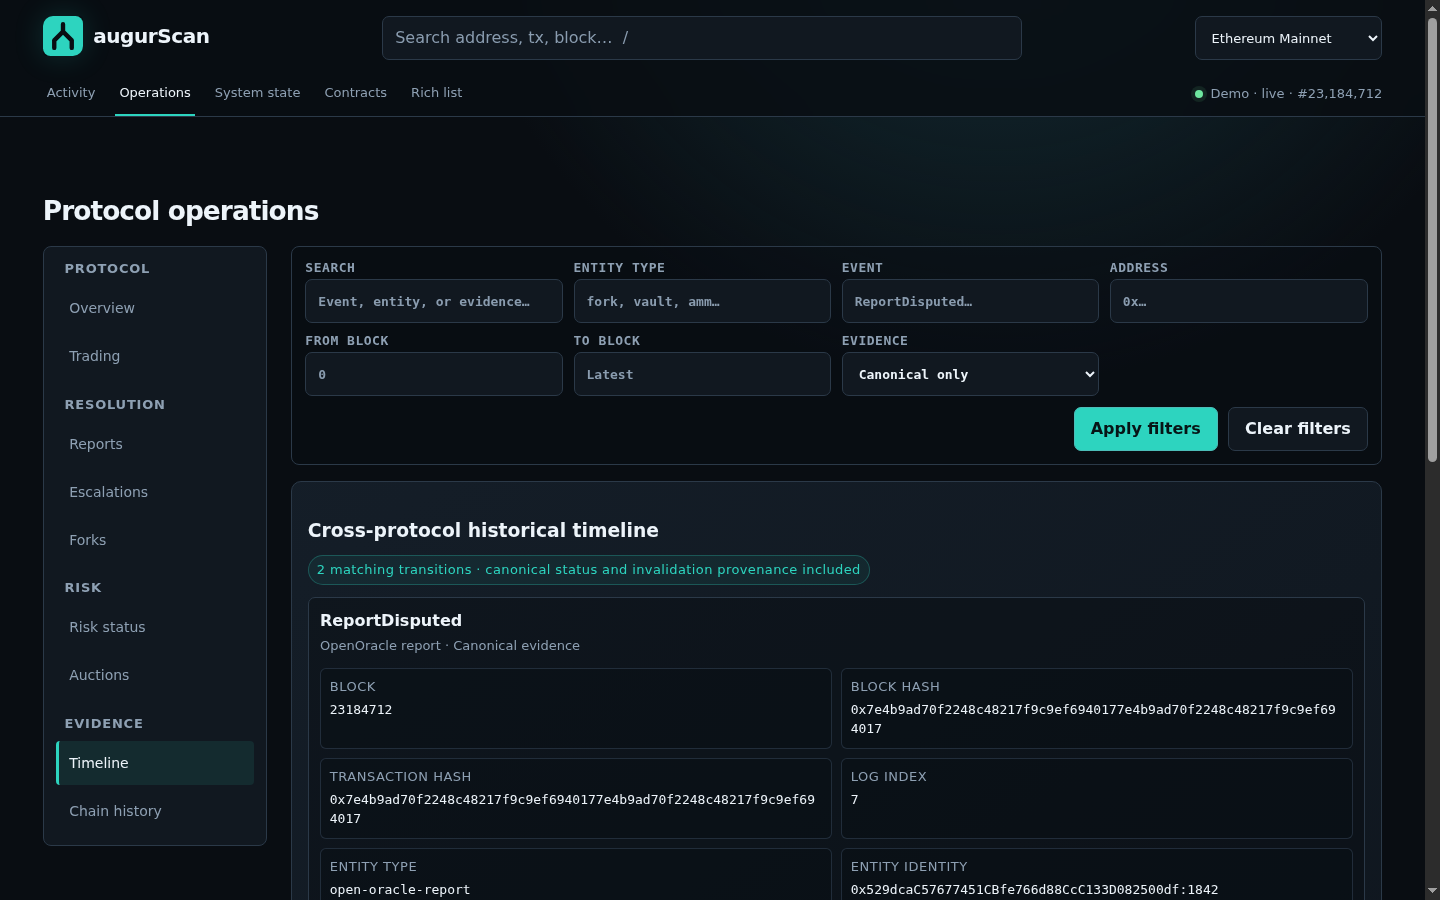
augurScan activity feed, unknown-chain notice, timeline filters (1440x900)
augurScan metric cards wrap (390x844)